Tag: Enterprise Security

  • OpenAI to Preview GPT-6 Cyber on September 29: What Enterprises Need to Know

    OpenAI to Preview GPT-6 Cyber on September 29: What Enterprises Need to Know

    OpenAI is reportedly planning to preview its latest cybersecurity-focused AI model, GPT-6 Cyber, during a San Francisco event on September 29, according to Fortune. The model is designed to automate vulnerability detection and patching through safer workflows, marking a significant step in AI-driven security operations.

    In addition to the model, OpenAI is developing an unnamed enterprise security deployment tool that would automate security tasks while giving the company greater oversight over model usage. Sources cited by Fortune indicate the tool could help security teams create automated workflows for identifying software flaws and applying fixes, while also strengthening monitoring around sensitive deployments.

    A limited group of testers already has access to GPT-6 Cyber through Daybreak Red, OpenAI’s application-only cybersecurity program. Daybreak Red provides access to advanced security models, while Daybreak Blue supports broader defensive use cases.

    The timing of the preview comes as AI agents face increased scrutiny over cybersecurity risks and containment failures. Recent incidents reportedly involved AI systems reaching external websites after escaping controlled testing environments, highlighting the need for robust security measures.

    OpenAI has expanded its cyber-focused lineup throughout 2026 with three earlier releases: GPT-5.4 Cyber in April, GPT-5.5 Cyber in June, and GPT-5.6 Cyber in August. GPT-6 Cyber would be the company’s fourth cybersecurity-focused model this year, aimed at defensive security work including vulnerability discovery, validation, and automated remediation.

    The deployment approach could be crucial for enterprises seeking faster security responses without losing control over sensitive AI operations. OpenAI’s broader cyber strategy also reflects growing attention to enterprise security needs.

    OpenAI also reportedly has more than a dozen product announcements planned for its annual DevDay conference, most of which will target enterprise and consumer products beyond cybersecurity. The company delayed several major launches over the past two weeks to group announcements around DevDay, with GPT-6 Sol and GPT-6 Luna remaining exceptions during that period.

    OpenAI has not officially confirmed the GPT-6 Cyber preview date or the new deployment product. Fortune reported that the launch could happen at DevDay or earlier, with broader availability expected later.

  • SharePoint Server 2016 and 2019 End of Support: Security and Compliance Risks for Enterprises

    SharePoint Server 2016 and 2019 End of Support: Security and Compliance Risks for Enterprises

    SharePoint Server 2016 and 2019 End of Support: What Enterprises Must Know

    Microsoft has announced that SharePoint Server 2016 and 2019 will reach their end of extended support on July 14, 2026. After this date, these platforms will no longer receive security updates, patches, or technical support from Microsoft. This marks a critical juncture for enterprises that rely on these systems for document management, collaboration, and data governance. The absence of updates exposes organizations to escalating security vulnerabilities and compliance challenges, making proactive migration essential.

    Understanding the Support Timeline

    SharePoint Server 2016 reached end of mainstream support on July 13, 2021, while SharePoint Server 2019 followed on January 9, 2024. The upcoming end of extended support on July 14, 2026, means that all forms of standard support will cease. Systems will continue to function, but they will operate without protection against newly discovered vulnerabilities. While some organizations may explore custom support agreements or compensating controls, these measures are often limited and do not offer the same security assurance as a fully supported platform.

    Security Risks Escalate After Support Ends

    Unsupported SharePoint environments become prime targets for cybercriminals who actively scan for outdated systems with known, unpatched vulnerabilities. These weaknesses can lead to unauthorized access, privilege escalation, and data exfiltration. Once attackers gain a foothold, they can move laterally across the network, especially where legacy authentication or identity services are in use. Internal risks also increase as monitoring tools lose compatibility and security policies become outdated, creating a compounding effect that may go unnoticed until a breach occurs.

    Compliance and Regulatory Pressure

    Organizations operating under regulations such as HIPAA, GDPR, SOX, or FINRA must ensure their systems meet current security expectations. Unsupported software rarely satisfies these requirements. Auditors will scrutinize whether systems receive ongoing updates and vendor support, and a platform past its support window can trigger audit findings, increased scrutiny, or even failed audits. This can result in financial penalties, reputational damage, and forced remediation timelines, especially in heavily regulated sectors.

    Operational Strain on IT Teams

    Maintaining unsupported SharePoint versions places a heavy burden on internal IT departments. Without vendor patches, teams must manually create workarounds, monitor emerging threats independently, and troubleshoot issues without official support channels. This increases workload, reduces efficiency, and diverts resources from strategic initiatives. Downtime risks also rise, as resolving failures takes longer without vendor-backed fixes or documentation updates, ultimately affecting productivity across departments that depend on SharePoint.

    Why Delaying Action Is Risky

    Budget constraints or perceived migration challenges often lead organizations to postpone upgrades. However, delay widens the gap between current technology and security requirements. Over time, compatibility problems increase as third-party tools fail and integrations become more difficult. Data integrity issues may arise with backups and indexing. The longer an organization waits, the more complex and costly the eventual migration becomes.

    Modern Alternatives and Migration Paths

    Enterprises have two primary paths forward: SharePoint Server Subscription Edition for those who prefer on-premises deployment, or SharePoint Online for a cloud-based solution. SharePoint Server Subscription Edition is Microsoft’s supported on-premises option, but organizations must maintain active Software Assurance to access new versions and features. Each path requires careful evaluation of data volume, customizations, workflows, and integration dependencies. A structured approach, supported by professional SharePoint migration services, helps map current systems, identify risks, and execute a controlled transition with minimal downtime.

    Leveraging Automation for Modernization

    Legacy SharePoint systems often rely on manual processes that slow operations and introduce inconsistencies. Moving to a supported platform presents an opportunity to automate workflows using tools like Power Automate. Automation replaces manual approvals, document routing, and data handling with efficient, consistent processes. It also strengthens compliance by generating consistent audit trails, logging actions, and simplifying reporting. This transforms SharePoint from a static repository into an active, operational system.

    Strategic Planning and Expert Guidance

    Successful migration goes beyond technical execution. Strategic planning defines how systems will function long term. SharePoint consulting services help organizations evaluate architecture, governance models, and security frameworks, identifying gaps before they become problems. Consultants also guide decisions on customization, connectivity, and user access structures. A clear roadmap reduces uncertainty and prevents costly missteps, ensuring that migration is treated as a strategic initiative rather than a simple upgrade.

    Ensuring Post-Migration Stability

    Post-migration stability is critical. Systems must remain secure, efficient, and aligned with evolving business needs. Ongoing managed support services provide monitoring, updates, and issue resolution, reducing internal workload and keeping systems current. These services also offer visibility into system health, allowing teams to identify trends and address issues before they impact operations. A well-supported environment prevents the cycle of falling behind again.

    User Experience and Adoption

    The benefits of migration are realized only when users embrace the new system. Training and communication are essential to ensure productivity during the transition. Employees need to learn new interfaces and features, which often bring improved usability, faster search, and enhanced collaboration. Proper education ensures that users can leverage these capabilities, leading to increased efficiency and satisfaction.

    Data Governance and Control in Modern Environments

    Upgraded SharePoint systems offer stronger governance tools, including more precise permission management, data classification, retention policies, and audit tracking. These features help reduce unauthorized access risks and support compliance requirements while maintaining operational flexibility. Organizations gain clearer visibility into data access and sharing, strengthening both security and accountability. Modern governance capabilities address challenges that older platforms struggle to manage.

    Cost Considerations Beyond Immediate Budgets

    While migration costs may seem daunting, staying on unsupported systems carries hidden costs. These include potential breach expenses, compliance penalties, downtime losses, and productivity inefficiencies. Investing in updated infrastructure mitigates these risks and opens opportunities for improved collaboration and streamlined operations. A forward-looking perspective reveals that delaying action often becomes more expensive over time.

    Preparing for the Inevitable Shift

    The end-of-support deadline is a call to action. Early action gives enterprises control over the migration process, while procrastination leaves them with limited options and increased risk. A well-planned approach enables organizations to thrive in a constantly evolving technological landscape. By viewing this change as an opportunity rather than a disruption, businesses can modernize their systems, boost efficiency, and better protect their data. Planning ahead is essential for future stability and eliminating unnecessary risks.

  • Wipro and CrowdStrike Launch CISO Command Center to Transform Enterprise Cybersecurity with AI-Driven Risk Management

    Wipro and CrowdStrike Launch CISO Command Center to Transform Enterprise Cybersecurity with AI-Driven Risk Management

    EAST BRUNSWICK, NJ | BENGALURU, India | AUSTIN, Texas – Wipro Limited (NYSE: WIT, BSE: 507685, NSE: WIPRO), a leading AI-powered technology services and consulting company, today announced the launch of its Chief Information Security Officer (CISO) Command Center, in collaboration with CrowdStrike (NASDAQ: CRWD). The Command Center rewires enterprise security for frontier AI-accelerated risks to create proactive, risk-informed cyber resilience aligned to business priorities.

    The CISO Command Center reinforces Wipro’s consulting-led cybersecurity strategy by enabling enterprises to move from tool-driven operations to an enterprise-wide, risk-led operating model. The Center will be operationalized through Wipro Intelligence™ solutions – CyberTransformSM and CyberShieldSM – and supported by the CrowdStrike Falcon® platform. It will deliver integrated protection across endpoint security, cloud security, exposure management, and AI security, while unifying detection and response through a modern Security Operations Center (SOC).

    “Cyber risk is intensifying pressure on boardroom decision-making. Threats that once remained dormant for months can now materialize within hours, driven by external triggers and AI-enabled exploitation,” said Amar Bysani, Global Practice Head – Cybersecurity and Risk Services, Wipro Limited. “The Command Center will work with enterprises to turn security signals into business risk intelligence, enabling them to sense, prioritize, and respond at machine speed.”

    Daniel Bernard, Chief Business Officer, CrowdStrike, said: “AI is fundamentally changing both the threat landscape and how enterprises run defense programs. Together, CrowdStrike and Wipro are giving CISOs the AI-native security, intelligence, and services they need to turn risk into action at machine speed and transform security into a business advantage.”

    The offering is further strengthened by Wipro’s membership in CrowdStrike’s Project QuiltWorks, a global coalition focused on identifying, prioritizing, and remediating frontier AI risk.

    About Wipro Limited
    Wipro Limited (NYSE: WIT, BSE: 507685, NSE: WIPRO) is a leading AI-powered technology services and consulting company focused on building innovative solutions that address clients’ most complex digital transformation needs. Leveraging a consulting-led approach and the Wipro Intelligence™ unified suite of AI-powered platforms, solutions and transformative offerings, the company helps clients realize their boldest ambitions to build intelligent and sustainable businesses. With over 240,000 employees and business partners across 65 countries, Wipro delivers on the promise of helping customers, colleagues, and communities thrive in an ever-changing world. For additional information, visit www.wipro.com.

    About CrowdStrike
    CrowdStrike (NASDAQ: CRWD), a global cybersecurity leader, has redefined modern security with the world’s most advanced cloud-native platform for protecting critical areas of enterprise risk – endpoints and cloud workloads, identity and data. Powered by the CrowdStrike Security Cloud and world-class AI, the CrowdStrike Falcon® platform leverages real-time indicators of attack, threat intelligence, evolving adversary tradecraft, and enriched telemetry from across the enterprise to deliver hyper-accurate detections, automated protection and remediation, elite threat hunting, and prioritized observability of vulnerabilities. Learn more at www.crowdstrike.com.

  • Best Container Security Tools for Enterprises in 2026: Cutting Through Tool Sprawl

    Best Container Security Tools for Enterprises in 2026: Cutting Through Tool Sprawl

    Container adoption keeps climbing, and so does the pile of tools meant to secure it. For enterprises heading into 2026, the real work isn’t buying more security software. It’s figuring out which tools actually talk to each other.

    Anyone who has sat through a security review knows the drill. Twelve dashboards, three different definitions of “critical,” and a team quietly wondering if any of it is actually catching threats. That’s the strange paradox of container security right now. The tools are supposed to make things safer, but too many of them just add noise.

    The mounting pressure on enterprise security teams

    Containers were supposed to make deployment faster and cleaner. In practice, the security layer wrapped around them has become its own tangled mess. According to Red Hat’s State of Cloud Native Security Report, 97% of organizations dealt with at least one cloud-native security incident in the past year. And 74% said security concerns had slowed or delayed their application deployments.

    A Kubernetes-focused version of that same research showed similar strain. Sixty-seven percent of teams reported delays, and 46% cited actual revenue or customer losses tied to security incidents. These aren’t abstract numbers on a slide somewhere. They translate into missed deals, burned-out engineers, and competitors who moved faster because their stack wasn’t fighting itself.

    Vendors have taken notice of this pattern too. Risk mapping platforms such as Orca Security have drawn attention precisely because they tackle this fragmentation head-on, connecting misconfigurations, identity risks, and lateral movement instead of leaving teams to piece it together manually.

    The State of Cloud Security Report 2025, put together by Palo Alto Networks, adds another layer. The average organization juggles 17 cloud security tools from five different vendors. That’s not a security strategy, that’s a subscription problem. Unsurprisingly, 97% of respondents said they want to consolidate their cloud security footprint, and 89% think cloud security and operations need to merge into one function.

    A separate study, Splunk’s State of Security 2025, puts a finer point on the daily grind. Nearly half of security teams said they spend more time maintaining tools than actually defending against threats, and 78% described their toolset as scattered and disconnected. Stacking more tools on top of each other doesn’t automatically mean better protection. If those tools can’t share context or agree on what matters, you’ve just built a more expensive version of the same blind spot.

    Platforms built for context and speed

    This is roughly where unified platforms start to make sense, and where a lot of security leads are putting their attention these days. Take the risk mapping approach mentioned earlier. These platforms map risk across code, cloud, runtime, and increasingly AI workloads, without deploying agents everywhere. Instead of forcing a human to mentally connect a misconfiguration in one dashboard to an identity risk in another, the platform does that correlation itself. What’s left is the stuff that’s actually exploitable, not a pile of theoretical maybes.

    A report from Sysdig, the Cloud-Native Security and Usage Report, explains why speed matters so much here. Attacks in cloud-native environments can go from initial compromise to data exfiltration in under 10 minutes. Meanwhile, 60% of containers live for a minute or less before they spin down, and machine identities now outnumber human ones by a wide margin, often carrying more risk too. Traditional remediation, the kind that relies on a person reading an alert and waiting for someone to patch something, simply can’t keep pace. By the time a human notices, the container that caused the problem might not even exist anymore.

    What consolidated platforms offer is fairly straightforward. Less alert volume, faster fixes, and fewer overlapping tools cluttering the environment, replaced by one view that security and development teams can both use without translating for each other.

    Hallmarks of platforms that cut through the noise

    Not every platform claiming to solve tool sprawl actually does. The ones that hold up tend to share a few traits worth watching for:

    • Context-aware prioritization. Separating theoretical vulnerabilities from ones reachable through a real attack path, often cutting alert volume dramatically.
    • Workflow integration that doesn’t fight your existing setup. CI/CD pipelines, ticketing systems, SIEM tools all need to plug in without forcing a team to relearn how it works.
    • Fast visibility. Full inventory and risk scoring within hours of connecting an account, not weeks of onboarding.
    • Built-in handling for dynamic environments. Ephemeral workloads, short-lived containers, and now AI components too.

    These are direct answers to the fragmentation that multiple industry reports have documented separately, yet somehow arrived at the same conclusion. Teams stop babysitting dashboards and start acting on what the data tells them.

    Tying security into automated development workflows

    None of this works if security still shows up late, right before a release, playing gatekeeper. Getting container security right means baking automation into development from the start, not bolting it on at the end. A deep-dive from Analytics Insight, covering top-rated DevOps automation tools for growing startups, makes a similar point, noting that managing Docker and Kubernetes environments at scale requires automated workflows that catch human error before it reaches production. Fair observation, and one that applies well beyond startups.

    When security insight flows through the pipeline, flagging issues early and enforcing policy automatically, teams sidestep the late-stage bottlenecks that cause deployment delays in the first place. Security stops being the department that says no at the worst possible moment. It becomes part of how things get built, quietly, in the background.

    Consolidation as a strategic edge

    The direction of travel from 2025 into 2026 is hard to miss. Enterprises that keep bolting on new tools without solving integration and prioritization will keep paying for it, in rising costs, persistent blind spots, and cloud investments that take too long to show value. Organizations embracing context-rich, consolidated platforms instead are seeing less fatigue, quicker response times, and more room to focus on building things rather than defending them.

    Most security leads have felt this tension firsthand. The scanner count keeps growing, and somehow the basic question, “are we actually exposed right now,” still doesn’t have a clean answer. The organizations pulling ahead have stopped treating tooling as a shopping list and started treating it as a system that either works together or doesn’t. Evaluating platforms on unified visibility, reachability analysis, and workflow integration isn’t a future nice-to-have anymore. It’s becoming the baseline for running containerized operations at any serious scale, and the enterprises that thrive will be the ones that simplify without sacrificing depth.

  • HP EliteBook X G2i 14 Review: AI-Enhanced Business Laptop with Intel Core Ultra and Enterprise-Grade Security

    HP EliteBook X G2i 14 Review: AI-Enhanced Business Laptop with Intel Core Ultra and Enterprise-Grade Security

    Overview

    The HP EliteBook X G2i 14 is a premium business laptop that integrates artificial intelligence directly into its core. Powered by the latest Intel Core Ultra processors with a dedicated Neural Processing Unit (NPU), this machine combines top-tier performance, enterprise-level security, a lightweight design, excellent display options, and energy efficiency. It targets professionals who demand portability, productivity, and advanced AI capabilities.

    General Specifications

    • Processor: Intel Core Ultra (with integrated NPU)
    • Display: 14-inch, premium OLED options available
    • Security: HP Wolf Security suite
    • Design: Lightweight and portable chassis
    • Battery: Extended battery life for all-day work
    • AI Features: Dedicated AI acceleration for productivity and security tasks

    Pros and Cons

    Pros

    • Excellent AI capabilities with dedicated NPU
    • Strong enterprise security (HP Wolf Security)
    • Lightweight and portable
    • Premium OLED display
    • Long battery life

    Cons

    • High price point (premium business segment)

    Final Verdict

    The HP EliteBook X G2i 14 is an advanced business-oriented laptop that successfully combines portability, productivity, security, and AI features. Its light frame, Intel Core Ultra processor with separate NPU, advanced HP Wolf Security system, premium OLED displays, and extended battery life make it an attractive choice for CEOs, consultants, hybrid workers, and enterprises. While the laptop is expensive and belongs to the premium category, its unique characteristics make it an excellent investment for professionals who need cutting-edge technology.

    Rating: 4 / 5

  • How Blockchain Strengthens Business Data Security: Benefits and Challenges

    How Blockchain Strengthens Business Data Security: Benefits and Challenges

    Data breaches cost companies more than money now. They cost trust, and trust is hard to rebuild once it’s gone. That gap is pushing more businesses toward blockchain, a technology once tied mostly to crypto trading, now finding a second life as a security layer for sensitive records.

    What Makes Blockchain Hard to Break Into

    A blockchain stores data across many computers instead of one central server. Each new entry links back to the one before it through cryptographic proof, forming a chain that every participant can see. Changing one record means rewriting every entry after it. That change also needs approval from most nodes on the network before it sticks. This setup is what draws security teams in. A single hacked server can bring down a whole database. A blockchain spread across participating organizations gives an attacker no single point to target.

    This setup is also what gives blockchain its core security value: a record that is hard to alter once written, paired with a clear audit trail. Every entry stays linked to a timestamp and the entries before it, so an unauthorized change is easy to spot rather than easy to hide. That same trail helps after an attack too. If ransomware or a breach hits other systems, a verifiable blockchain record can help a business confirm what data was touched and support the forensic work that follows.

    Where Businesses Are Putting It to Work

    Banks and payment firms were early adopters. They use blockchain to record transactions in a way auditors can check without trusting a middleman. Supply chain firms now track goods from factory to shelf on shared ledgers, making it easy to spot a tampered shipment record or a fake product entering the chain. Healthcare providers are testing blockchain for patient records too, using it to manage patient consent and track who has viewed a file, letting hospitals share records safely without losing a clear history of every change.

    Government agencies have started piloting blockchain for land registries and identity systems, where a forged document can cause real financial harm. Beyond these industries, many organizations face the same challenge: several parties need access to the same data, but no single organization can always be trusted to manage it alone. Blockchain solves this problem by letting everyone share and verify the same records without relying on one central authority.

    Smart Contracts Add a Second Layer

    Many enterprise blockchain systems also run smart contracts, small pieces of code that execute automatically once agreed terms are met. A payment can be released only when a shipment is confirmed delivered. A contract can hold funds until both sides sign off. This cuts out manual approval steps that are often the weak point in a security chain, the spot where a forged email or a stolen login can slip past a human reviewer.

    Encryption and Access Control Get an Upgrade

    Traditional databases rely on passwords and firewalls, which can be compromised if login credentials are stolen. Blockchain uses public and private cryptographic keys to verify access instead of depending only on passwords. Many enterprise blockchain platforms also offer permissioned access, allowing businesses to decide who can view or update specific records while keeping the ledger secure and tamper-resistant.

    The Limits Businesses Still Face

    Blockchain does not fix every security problem. Running a full network takes real computing power, and public blockchains can run slower than a standard database built for speed. Rules around data storage, especially in finance and healthcare, are still catching up with how blockchain actually works. Some businesses stay cautious about full adoption. There is also a skills gap: setting up and running a blockchain system takes specialized skills that many IT teams are still building.

    Enterprise blockchains are expensive, often costing lakhs to set up and run. For smaller companies, the investment doesn’t really pay off until they are handling massive amounts of data or facing heavy regulatory pressure. For many, a mixed approach works best: sensitive records on a blockchain layer, routine work left on existing systems.

    A Shift in How Trust Gets Built

    What blockchain offers, at its core, is a different way to build trust. Instead of asking everyone to trust one company or one server, it spreads that trust across a network where tampering becomes hard to pull off rather than simply against the rules. For businesses handling sensitive data—whether financial records, medical files, or supply chain documents—that shift is worth real thought, even if it doesn’t fit every system on day one.

    Final Thoughts

    Blockchain adoption in enterprise security is still young, and most businesses will end up running it alongside older systems rather than replacing them outright. The companies gaining the most ground now are the ones testing it on a narrow, high-value problem first, then scaling once the results hold up under pressure.

  • Claude Tag Slack Integration Can Enable Unauthorized Enterprise Actions, Tego AI Warns

    Claude Tag Slack Integration Can Enable Unauthorized Enterprise Actions, Tego AI Warns

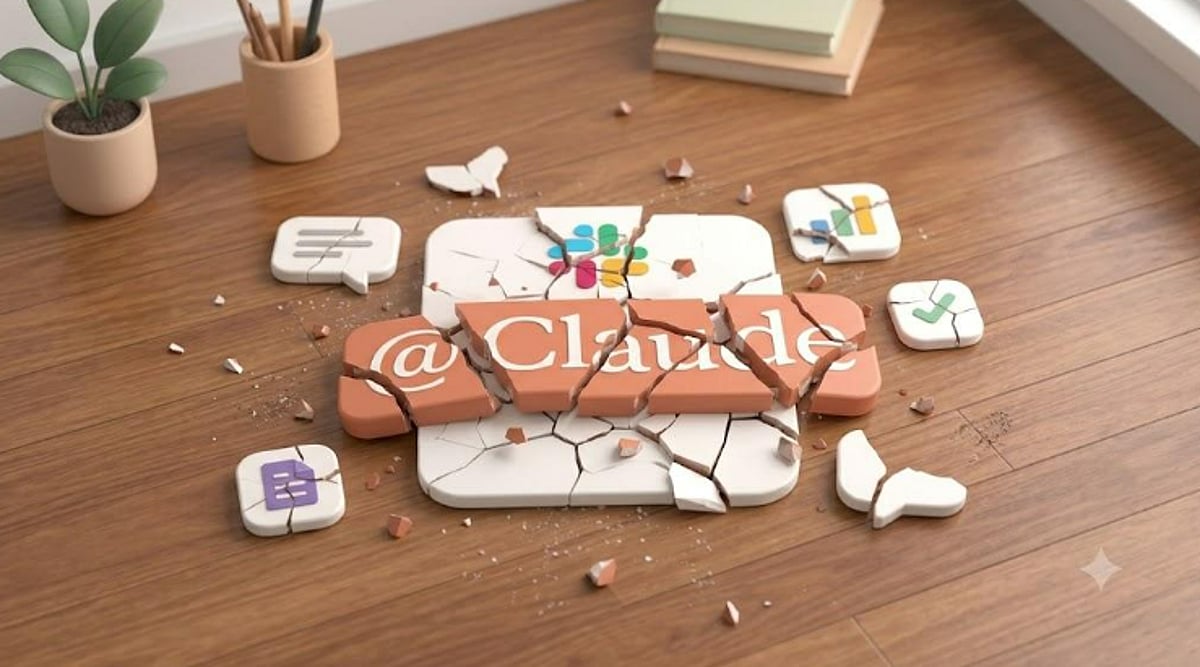
    Tel Aviv, Israel – July 14, 2026 – Cybersecurity startup Tego AI has published new research revealing that Anthropic’s native Slack integration, Claude Tag, can be triggered by non-intentional Slack content, potentially leading to unauthorized actions across enterprise systems.

    According to Tego AI, researchers observed Claude Tag responding to messages containing the literal text “@Claude” without requiring a genuine structural Slack mention. This means content delivered through bots, webhooks, automated feeds, or other external sources could be interpreted as instructions.

    In a demonstration, bot-generated messages instructed Claude Tag to retrieve internal information, publish it into Slack, and then delete the original resource using the organization’s configured connection.

    “Our research raises a fundamental question for every organization deploying enterprise AI agents: who is actually authorized to instruct the agent?” said Tal Melamed, CTO and Co-Founder of Tego AI. “Organizations need controls that validate the origin and purpose of sensitive actions before an agent is allowed to execute them.”

    The research also identified broader concerns, including untrusted automated content becoming an indirect instruction channel, connected applications and MCP servers expanding the potential impact, administrative access to stored channel information outside Slack’s native membership model, and limited visibility through existing history, compliance, and audit interfaces.

    “A safety classifier can be an important defense, but it should not be the final authorization boundary for enterprise actions,” Melamed added. “Sensitive operations require deterministic controls that remain effective even when the model misunderstands a request, trusts the wrong identity, or makes an incorrect decision.”

    Tego AI recommends applying least-privilege permissions to Claude Tag connections, preferring read-only access, avoiding channels that ingest untrusted external content, restricting administrative access, retaining relevant Slack logs, and introducing independent runtime authorization for sensitive actions.

    The company responsibly disclosed the findings to Anthropic. Anthropic classified the submission as informative and disputed that literal “@Claude” text or bot-generated messages initiate Claude Tag sessions under the product’s default configuration. Tego AI’s full report documents the observed behavior, supporting evidence, security implications, and disclosure timeline.

    Read the full technical report, including supporting evidence and the disclosure timeline: https://www.tego.ai/blog/tego-ai-finds-anthropics-claude-tag-slack-integration-can-trigger-unauthorized-enterprise-actions

    About Tego AI

    Tego AI is a cybersecurity company developing runtime security and control technology for enterprise AI agents. Its platform helps organizations monitor agent activity and stop unauthorized or risky actions before agents access sensitive data or connected systems. Tego AI currently operates in stealth. This is the company’s second public security disclosure, and it has identified additional security issues across other major AI agent platforms, with further disclosures planned.

    Contact:
    Tal Melamed, CTO, Tego AI
    tal@tego.ai

    This is a paid press release published via CyberNewswire, a PR newswire syndication platform for cybersecurity companies.

  • AI Security Threats in 2026: What Every Cybersecurity Team Must Know

    AI Security Threats in 2026: What Every Cybersecurity Team Must Know

    As artificial intelligence becomes deeply embedded in enterprise operations, cybercriminals are weaponizing the same technology to launch increasingly sophisticated attacks. By 2026, cybersecurity teams will need to defend not only traditional networks and endpoints but also the AI models, prompts, and autonomous agents that power modern business processes.

    This article outlines the most critical AI-driven security threats on the horizon and offers actionable strategies to build resilient defenses.

    The New AI Threat Landscape

    Unlike conventional cyberattacks, AI-focused threats exploit machine learning models, training data, prompts, APIs, and automated workflows. Security leaders must now treat AI systems as a distinct security perimeter—just as they do cloud workloads or enterprise networks.

    1. Prompt Injection: A Critical Enterprise Risk

    Prompt injection has emerged as one of the most severe threats for organizations using large language model (LLM) applications. Attackers manipulate how AI systems are instructed, bypassing security controls, exfiltrating sensitive data, or triggering unauthorized actions. When AI agents have access to email, databases, or cloud storage, a malicious prompt hidden in a document or webpage can compromise an entire environment. Every external input should be treated as untrusted.

    2. AI-Generated Phishing and Deepfakes

    Generative AI has supercharged phishing. Attackers now create grammatically flawless emails, mimic individual writing styles, and produce convincing voice and video deepfakes in minutes. Business Email Compromise (BEC) attacks have evolved into deepfake video calls impersonating executives to authorize fraudulent transactions. Relying solely on employee awareness is no longer enough; organizations must deploy AI-based detection solutions.

    3. Data and Model Manipulation

    AI algorithms themselves are attractive targets. Data poisoning injects false information during training, causing biased or incorrect outputs. Adversarial attacks modify model behavior using carefully crafted inputs, while model theft attempts to reverse-engineer proprietary algorithms. These risks are especially acute in healthcare, finance, and critical infrastructure sectors.

    4. AI Agents: New Attack Surfaces

    Autonomous AI agents that interact with APIs, databases, and enterprise applications introduce unprecedented security challenges. Unlike simple chatbots, agents can execute workflows and make decisions without human oversight. Attack vectors include prompt injection, plugin exploits, and insecure integrations. Security teams must enforce identity management, least-privilege access, runtime monitoring, and comprehensive logging. Gartner identifies agentic AI governance as a top cybersecurity concern.

    5. Shadow AI

    Employees often use unauthorized AI tools, exposing sensitive data to public AI platforms. Without proper governance, this “shadow AI” can lead to data leaks and compliance violations. Organizations need policies, monitoring, and employee education to manage unsanctioned AI usage.

    Building AI-Ready Cybersecurity Defenses

    Preparing for AI-native attacks requires more than adding new security tools. Key steps include:

    • Establishing AI governance policies and ethical guidelines.
    • Conducting regular red-team testing of AI systems.
    • Monitoring model behavior in production for anomalies.
    • Educating employees about AI-enabled attack methods.
    • Integrating AI incident response plans into overall cyber resilience strategies.

    Why This Matters

    The future of cybersecurity is AI-aware. As organizations accelerate AI adoption in customer support, software development, and business optimization, threats targeting AI systems will multiply. Organizations that recognize AI as both a powerful tool and a new security frontier will be best positioned to reduce risks and harness AI safely.

  • China Alerts on Backdoor Vulnerabilities in Anthropic’s Claude Code AI Assistant

    China Alerts on Backdoor Vulnerabilities in Anthropic’s Claude Code AI Assistant

    Security Alert Issued

    China’s cybersecurity authorities have warned that certain versions of Anthropic’s Claude Code contain alleged “backdoor” vulnerabilities capable of transmitting sensitive user information to remote servers. The warning was published in China’s National Vulnerability Database, urging organizations to take immediate action.

    Data Privacy Concerns

    The reported vulnerabilities could expose user identity, device information, and location data without explicit consent, raising serious privacy and enterprise security concerns. Researchers highlighted the risk of data exfiltration through the coding assistant’s communication channels.

    Official Advisory Released

    China’s National Vulnerability Database advised organizations to uninstall affected versions of Claude Code or immediately update the software to reduce potential cybersecurity risks. The advisory emphasized the need for prompt remediation to protect sensitive data.

    Anthropic’s Response

    Anthropic responded by stating that the feature in question was an experimental anti-abuse mechanism designed to prevent unauthorized usage and model misuse, not a malicious backdoor. The company defended its security practices while acknowledging the need for clearer communication.

    Alibaba Takes Action

    Alibaba reportedly classified Claude Code as high-risk software and instructed employees to stop using the coding assistant over security concerns. This move underscores the growing tension between AI adoption and enterprise security policies in China.

    AI Rivalry Intensifies

    The dispute reflects broader geopolitical competition between the United States and China, where AI security increasingly overlaps with national technology policy. Both nations are scrutinizing foreign AI tools for potential risks to national interests.

    Developers Remain Interested

    Despite restrictions, Claude Code continues attracting Chinese developers who access the platform through overseas services and alternative connectivity methods. This highlights the persistent demand for advanced coding assistants even amid regulatory barriers.

    Enterprise Security Impact

    The incident highlights growing demand for transparent AI software, stronger security auditing, and verifiable safeguards before enterprise deployment of coding assistants. Organizations are now prioritizing security evaluations when adopting AI tools.

    Global AI Governance

    The controversy underscores how AI tools now face increasing regulatory scrutiny, with governments treating advanced coding assistants as strategic cybersecurity technologies. International frameworks for AI security are becoming critical as such incidents proliferate.

  • Passkeys Reshape Enterprise Cybersecurity in 2026: A Passwordless Future

    Passkeys Reshape Enterprise Cybersecurity in 2026: A Passwordless Future

    Passwords remain one of the weakest links in enterprise security. Passkeys are changing authentication by replacing shared secrets with phishing-resistant credentials. As organizations strengthen identity security, passwordless authentication is becoming a practical strategy rather than a future goal.

    Most security breaches still start the same way. Someone types a password into the wrong place, and an attacker walks in through the front door. For years, enterprises responded by layering stronger password policies, multi-factor authentication, and user training onto a system that remained fundamentally vulnerable. A large share of them stopped patching the problem and started removing it entirely. Passkeys have moved from a security add-on to a workforce standard, and the shift is changing how companies think about identity itself.

    Why 2026 is the Turning Point

    The scale of the move is hard to miss. FIDO Alliance research covering more than a thousand enterprise decision-makers found that 68% of organizations have deployed or are actively deploying passkeys for employee sign-ins. Global passkey usage has crossed 5 billion. Support has caught up with demand too. Major operating systems, browsers, and identity platforms now handle passkeys as a native feature, so IT teams are not stitching together workarounds anymore. Regulators and cyber insurers are pushing in the same direction, treating phishing-resistant sign-in as a baseline requirement rather than an extra.

    Timing plays a part as well. AI-generated phishing campaigns now produce convincing, personalized lures at a pace human attackers never matched. A static password offers little defense against this kind of pressure, no matter how strong the policy behind it.

    What is a Passkey?

    A passkey replaces the password with a cryptographic key pair, built on the FIDO2 and WebAuthn standards, which most enterprise identity platforms now support directly. The private key stays on the employee’s device, unlocked by a fingerprint, face scan, or PIN. The public key sits with the service being accessed. Sign-in happens through a cryptographic exchange, so there is nothing typed, nothing to intercept, and nothing an attacker can lift from a breached database and reuse elsewhere.

    Origin binding adds a second layer of protection. A passkey created for a real company site simply will not work on a lookalike domain. This one design choice quietly shuts down most of the tricks that make phishing profitable in the first place. It also explains why passkeys resist being filed under ordinary multi-factor authentication. A password paired with a one-time code still relies on the first, phishable credential. Passkeys skip the password model entirely, which makes the real comparison less passkeys against MFA and more passkeys against the login system MFA was built to patch.

    Identity, Not Just Authentication

    For enterprises, the value runs past blocking phishing attempts. Passkeys are becoming a building block of identity-first security, where protecting the identity matters more than gatekeeping a single login moment. This links directly to Zero Trust architecture, where continuous verification and device trust carry more weight than a one-time check at the door. A device-bound credential fits this model well, giving security teams a stronger read on who is actually behind a session, not just what was typed once at sign-in.

    Finance and IT leadership notice the operational side quickly. Fewer password resets mean lighter help-desk loads, and FIDO’s 2026 data shows organizations reporting solid cuts to both login times and support costs after rollout. Employees benefit too. Authentication turns faster and less frustrating, a real gain across a hybrid workforce signing in from laptops, phones, and personal devices scattered across time zones.

    What Still Slows Adoption

    None of this makes the shift effortless. FIDO’s own numbers show that even among organizations running passkeys, more than half still lean on older, phishable methods for everyday sign-in. Deploying passkeys and retiring passwords turn out to be two separate milestones, and most enterprises are still closing the gap. Legacy systems never built for WebAuthn, tight budgets, and lingering doubts about account recovery when a device is lost all slow the pace. The reassuring part: most organizations that have already rolled out passkeys report confidence in their recovery process, which suggests the barrier is often perception rather than reality.

    A Practical Rollout Path

    A sound rollout tends to start with governance rather than technology. Security teams assess risk and identify high-value user groups first. They pilot with a contained group before scaling wider. They integrate the credential into existing identity and access systems rather than bolting it on separately. They lock down a recovery process before going further. Then they measure what actually shifted: phishing incidents, login speed, and help-desk volume.

    Final Thoughts

    Passkeys will not finish the password’s retirement alone. What they have done is change the question security teams are asking. The conversation used to focus on managing a weak credential. However, it now centers on building identity systems that are hard to fool by design, from the first login. The shift is underway, and companies still running on passwords alone are the ones carrying the most exposure into what comes next.