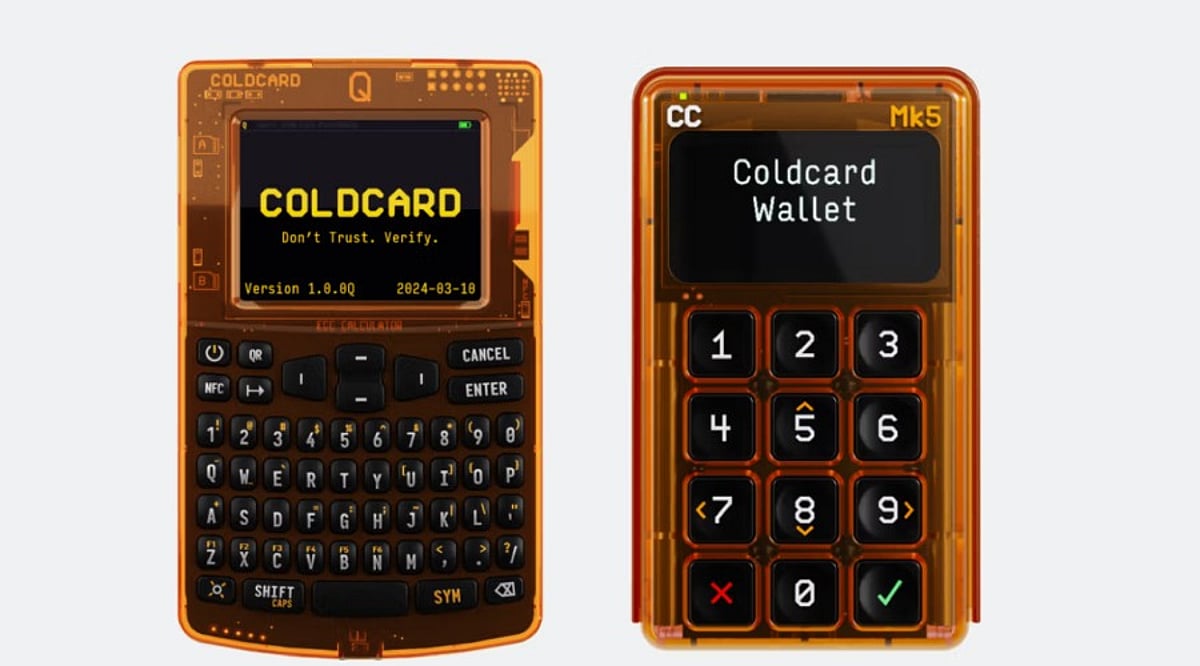
Galaxy Research has linked a firmware flaw in Coldcard hardware wallets to the theft of 1,082.65 Bitcoin, worth approximately $70 million. The coordinated withdrawals, which occurred across 1,196 addresses on July 30, took place within just 41 minutes, marking one of the largest reported hardware wallet incidents this year.
Galaxy Tracks a Coordinated Bitcoin Theft
Galaxy Research identified a consistent transaction pattern across the stolen funds, pointing to a single attacker behind the operation. However, the firm cautioned that the observed transfers may not include all exposed wallets. Other vulnerable addresses could remain inactive or be moved later. Blockchain records cannot distinguish between theft and a legitimate owner transfer when both use valid private keys, leaving the true extent of the breach uncertain.
Coinkite Expands Warning Across Coldcard Models
Coinkite initially warned owners of Coldcard Mk3 devices running firmware version 4.0.1, released in March 2021, that seeds created with the affected software could expose user funds. The company later widened the advisory to include selected firmware versions on Coldcard Mk4, Mk5, and Coldcard Q devices. Emergency updates were issued for every impacted model. Coinkite CEO Rodolfo Novak (NVK) accepted responsibility and apologized to customers, stating that the company’s internal review process failed to catch the defect before release.
AI-Assisted Analysis Raises New Security Concerns
Novak suggested that attackers may have discovered the flaw through artificial intelligence-assisted code analysis. Such tools can detect subtle weaknesses faster than traditional manual reviews, creating a growing challenge for software developers. While AI can help defenders inspect code, it also shortens the path from public release to exploitation.
What Affected Users Should Do
Coinkite urged affected users to take the following steps:
- Install the latest firmware version.
- Create new wallet seeds.
- Move Bitcoin into new wallets after testing small transfers first.
- Keep original backups until every transfer succeeds.
Coldcard wallets store private keys offline, but firmware bugs, supply chain risks, and configuration errors can still create attack paths. Galaxy Research linked the July 30 theft to vulnerable Coldcard wallet seeds across affected firmware versions. Coinkite released emergency updates and told users to create fresh seeds, test new wallets, and transfer funds while keeping original backups until every move succeeds.