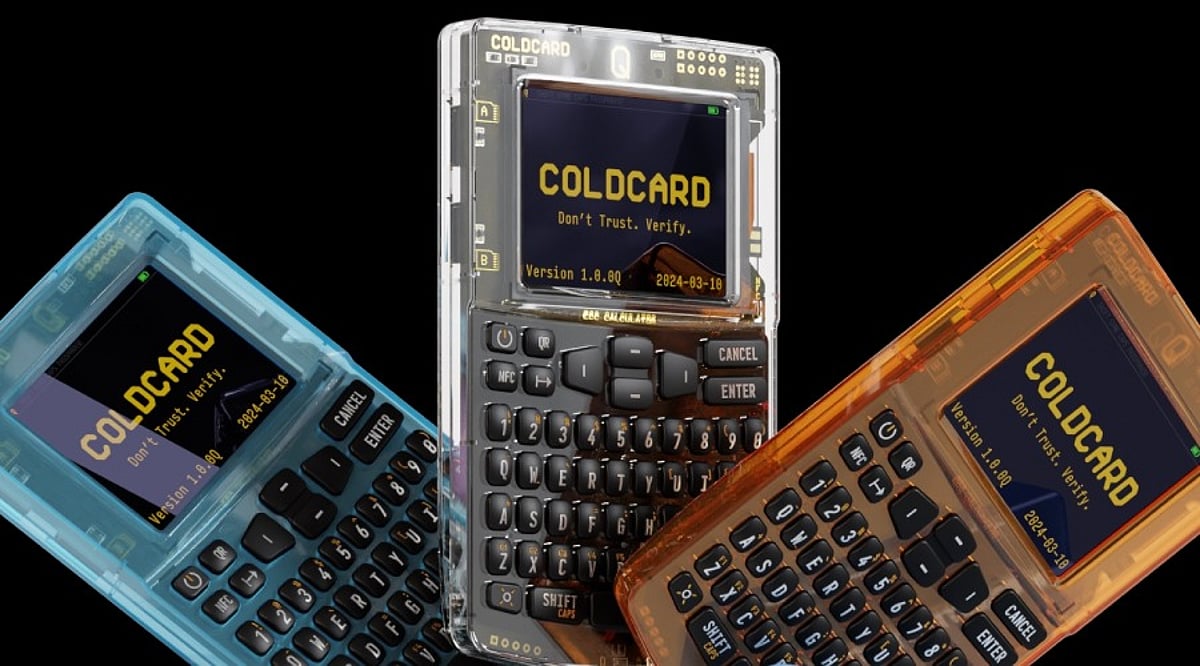
A series of hacks targeting Coldcard hardware wallets has reignited concerns about cryptocurrency self-custody, proving that even offline devices can fall prey to software vulnerabilities. According to blockchain security firms, hackers stole an estimated 1,596 BTC (worth roughly $130 million) from around 7,300 affected addresses, marking one of the largest hardware wallet security incidents in recent years.
The exploit does not mean Bitcoin’s cryptography has been compromised. Instead, researchers say attackers exploited a weakness in certain Coldcard firmware versions that produced insufficient randomness when generating seed phrases, making them predictable.
Firmware Vulnerability Enabled Seed Phrase Prediction
Hardware wallets are widely regarded as one of the safest ways to store digital assets because private keys remain offline. However, security researchers at Block discovered that some Coldcard devices generated seed phrases using weak entropy. This allowed attackers to reconstruct private keys through brute-force methods.
Blockchain analytics firm K33 reported that the attacks triggered an unusual spike in on-chain activity: approximately 890,000 BTC moved across the Bitcoin network over the past week—the highest weekly total recorded this year. K33 noted, “Therefore, the recent acceleration in BTC transaction activity is very likely driven by the Coldcard attacks.”
Victims believed they followed industry best practices. One affected user, Jonathan Goodman, who lost $1.6 million, wrote on X, “I never shared my seed phrase with anybody. My devices never touched the internet.” He added that the vulnerability originated from “one line in their code from 2021.”
What the Incident Means for Hardware Wallet Users
The vulnerability is specific to certain Coldcard wallet implementations and does not compromise Bitcoin itself—only the wallet implementation. So far, no evidence suggests that hardware wallets from manufacturers like Ledger, Trezor, BitBox, Foundation, Cypherock, or KeepKey share the same flaw.
After the announcement, Coinkite (Coldcard’s manufacturer) recommended that affected users immediately upgrade their firmware and create a new wallet using a fresh seed phrase. Restoring the old recovery phrase would not eliminate the susceptibility.
The incident has also brought multi-signature (multisig) wallets back into focus. Multisig setups require approvals from several devices before funds can be transferred, greatly mitigating the risk if any single device is compromised.
Why This Matters
The Coldcard exploit proves hardware wallets are not foolproof. Flawed seed phrase generation exposed offline funds, highlighting that true crypto security requires constant firmware updates, multi-signature setups, and multi-layered protection rather than relying on a single device.
Final Thoughts
TRM Labs reports that the crypto sector has experienced over 200 hacks so far in 2026, totaling more than $950 million in losses. The Coldcard event underscores that hardware wallets remain one of the most secure storage solutions available, but security is a matter of layers: keeping firmware updated, using strong seed phrases, spreading assets, and monitoring security advisories. Ultimately, this attack serves as a stark reminder to long-term Bitcoin investors that cybersecurity is not a one-time setup, but an ongoing journey.
Frequently Asked Questions
- What caused the Coldcard hardware wallet hack? The attack stemmed from a firmware vulnerability that generated predictable seed phrases due to insufficient randomness. This allowed attackers to reconstruct private keys without breaking Bitcoin’s underlying cryptography.
- Does this mean all hardware wallets are unsafe? No. The vulnerability appears specific to certain Coldcard firmware versions. There is currently no evidence that major brands like Ledger, Trezor, BitBox, Foundation, Cypherock, or KeepKey are affected by the same flaw.
- What should affected Coldcard users do immediately? Update the device to the latest firmware, generate a completely new wallet with a fresh seed phrase, and transfer Bitcoin to the new wallet. Simply restoring the old seed phrase does not eliminate the vulnerability.
- What is a multisignature (multisig) wallet, and why is it safer? A multisig wallet requires approvals from two or more devices or private keys before funds can be transferred. This significantly reduces theft risk because compromising one wallet is insufficient to access assets.
- What lessons can Bitcoin holders learn from the Coldcard incident? This attack highlights that hardware wallets remain highly secure but should not be the only layer of protection. Keeping firmware updated, securely backing up seed phrases, following official security advisories, and considering diversified custody or multisig setups can greatly improve long-term security.