
Tag: critical infrastructure

  • New AI Predictive Model Aims to Shift Cybersecurity from Reactive to Proactive for Critical Infrastructure

    New AI Predictive Model Aims to Shift Cybersecurity from Reactive to Proactive for Critical Infrastructure

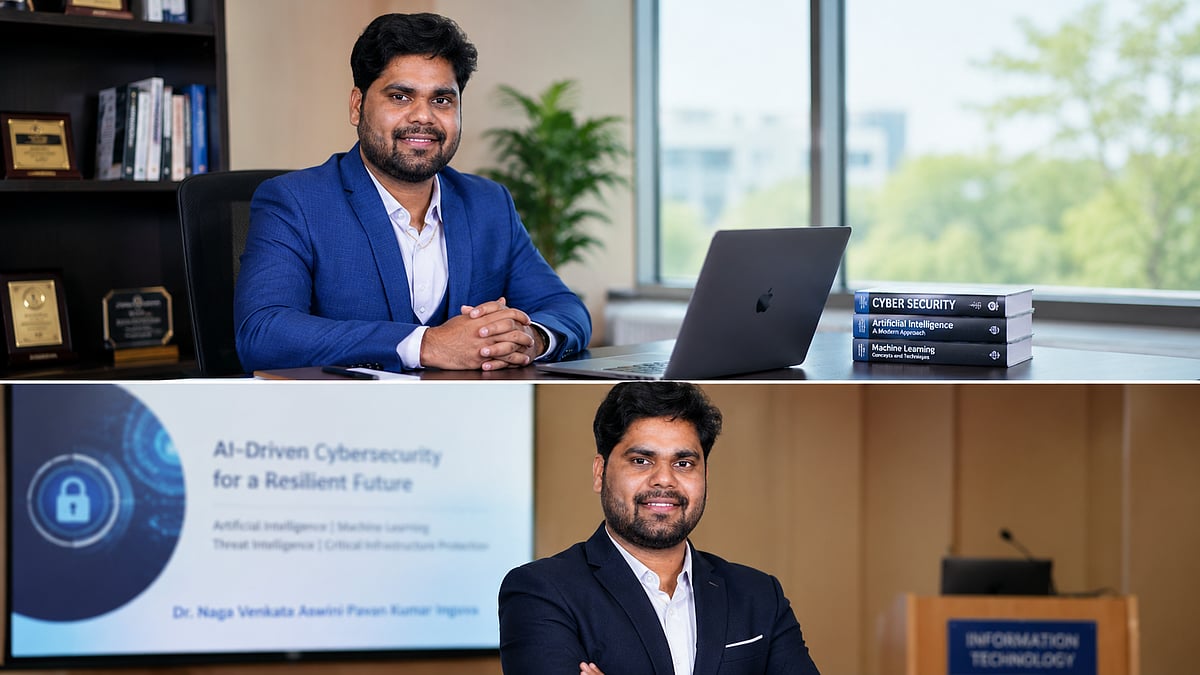
    For most public institutions, cybersecurity follows a predictable sequence: an incident occurs, a tool detects it, an alert is generated, and a team responds. According to Dr. Naga Venkata Aswini Pavan Kumar Inguva, a researcher and senior software developer at a U.S. state government agency, that order fundamentally puts organizations behind attackers from the start.

    Inguva argues that while this reactive approach may work for private companies, the stakes are far higher for public utilities such as water systems, hospitals, transit authorities, and power grids. In these sectors, a breach doesn’t just cost data or money; it disrupts essential services that people rely on with no alternative. He believes cybersecurity must move beyond rapid response toward anticipation.

    To address this, Inguva developed a conceptual framework for AI-driven predictive cyber threat intelligence. Unlike traditional detection systems that look for known attack patterns, his framework emphasizes contextual analysis—understanding the sequence and relationships between events to predict where an attack is heading. The research, which is a structured foundation rather than a deployed product, focuses on enterprise and critical infrastructure environments. It analyzes which machine learning techniques are genuinely applicable to threat prediction and provides recommendations for implementation.

    Public institutions, Inguva notes, present the hardest case: they often run aging technology, operate under tight budgets, and carry obligations private firms don’t. Their security spending tends to focus on monitoring, which produces volume but not foresight. His prescription is for a proactive, intelligence-driven, and context-aware posture paired with secure architecture, continuous monitoring, employee awareness, and proactive risk management.

    Inguva emphasizes that this is not solely a technical challenge. Protecting critical infrastructure requires shared responsibility across researchers, industry, and policymakers. His broader research record includes published work on generative adversarial networks, deep learning for threat detection, and machine learning for attack classification, some of which earned best paper awards. He is also a published author and co-founder of Thaapasi Smart Infratech Pvt. Ltd.

    Looking ahead, Inguva expects advances in artificial intelligence, graph analytics, threat intelligence, and automation to help organizations recognize attack progression earlier and prioritize genuine threats. But he stresses that these tools will not eliminate the need for skilled personnel, sound governance, and continuous learning.

    The core idea is a shift in sequence: a system built to react will always answer the attacker’s question first. Changing that order, Inguva argues, is the work worth doing.
  • Essential ICS/OT Cybersecurity Books for 2026: Protecting Critical Infrastructure

    Essential ICS/OT Cybersecurity Books for 2026: Protecting Critical Infrastructure

    The rapid evolution of digital infrastructure has simultaneously amplified cybersecurity threats, particularly targeting Operational Technology (OT) and Industrial Control Systems (ICS). As nation-state actors, ransomware groups, and AI-driven campaigns increasingly target the backbone of global economies, understanding industrial cybersecurity has become paramount. This guide highlights the most influential ICS/OT cybersecurity books of 2026, offering professionals both technical strategies and executive-level frameworks to safeguard critical operations.

    Quick Overview

    These essential resources cover industrial threat intelligence, compliance frameworks, ransomware defense, governance, and practical strategies. They help professionals strengthen critical infrastructure security against rapidly evolving cyber threats. Key topics include:

    • Threat Landscape Analysis: Understanding trending attack vectors such as ransomware and AI-driven attacks to assess potential costs of downtime and security breaches.
    • Frameworks & Standards: Latest standards like ISA/IEC 62443, NIST SP 800-82, and EU NIS2 provide crucial knowledge for applying defense mechanisms in industrial contexts.
    • Governance & Risk Ownership: Aligning OT risk with enterprise risk management for better capital allocation and product strategy.
    • Industry-Specific Strategies: Tailored approaches for sectors like energy, manufacturing, water, and chemicals addressing specific threats.
    • Vendor & Technology Insights: Analysis of tools and platforms for network monitoring, anomaly detection, and endpoint protection.

    Risks and Challenges

    Misclassification of OT incidents as IT events can delay response, leading to major financial losses and data breaches. AI-scaled threats accelerate vulnerability and exploitation. Compliance penalties (e.g., NERC CIP) can impose fines up to $1M per day for non-compliance. Operational impact includes audits, reputational damage, and forced shutdowns. Supply chain vulnerabilities require SBOM and secure-by-design adoption.

    Final Thoughts

    OT risk is now a boardroom priority. The consequences of industrial cybersecurity oversight include ransomware attacks, AI-driven intrusions, compliance penalties, and operational disruptions. By aligning CISOs and boards around governance, frameworks, and vendor strategy, organizations can transform cybersecurity from reactive defense into proactive resilience. The future of industrial security is about safeguarding trust, continuity, and the backbone of modern industry.

    Frequently Asked Questions

    1. Why are ICS/OT cybersecurity books important in 2026?

    They help professionals understand evolving industrial cyber threats, compliance requirements, ransomware defenses, and best practices for protecting critical infrastructure from increasingly sophisticated attacks.

    2. Which cybersecurity frameworks are commonly covered?

    Most leading books cover ISA/IEC 62443, NIST SP 800-82, NERC CIP, and the EU NIS2 Directive for securing industrial environments.

    3. Who should read these books?

    They are ideal for CISOs, OT security engineers, plant managers, industrial automation professionals, cybersecurity analysts, compliance officers, and policymakers responsible for critical infrastructure security.

    4. Do these books include real-world case studies?

    Yes, many feature case studies on ransomware attacks, nation-state threats, supply chain compromises, and lessons learned from major industrial security incidents.

    5. How can these books help improve industrial cybersecurity?

    They provide practical guidance on risk assessment, incident response, governance, Zero Trust implementation, regulatory compliance, and securing legacy and modern OT environments.