Tag: multi-factor authentication

  • 7 Essential Strategies to Safeguard Your Cryptocurrency

    7 Essential Strategies to Safeguard Your Cryptocurrency

    Cryptocurrency security is paramount in a digital landscape where threats evolve constantly. Whether you’re a seasoned investor or new to crypto, implementing robust protective measures can prevent theft and loss. Below are seven critical steps to keep your digital assets safe.

    Use a Hardware Wallet

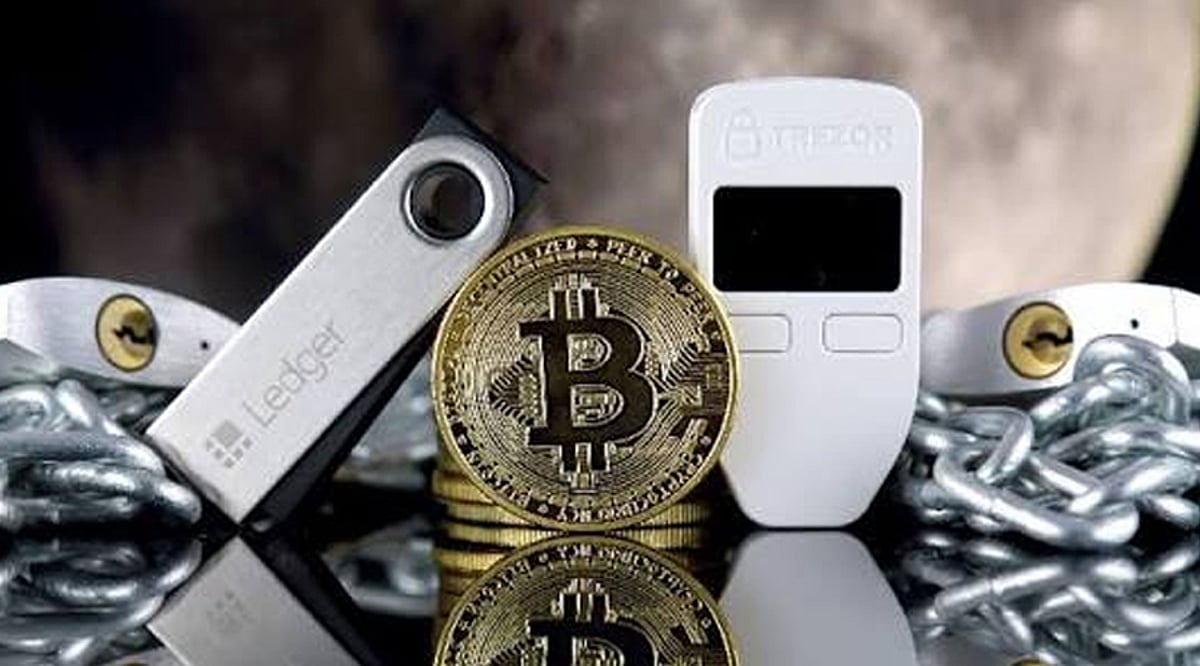
    Hardware wallets keep cryptocurrency private keys offline, reducing exposure to online threats. Devices such as Ledger and Trezor provide an additional security layer for long-term holdings. Always purchase wallets from official sources, protect recovery phrases carefully, and follow the manufacturer’s security instructions when setting up and accessing your assets.

    Secure Your Private Keys

    Private keys provide access to cryptocurrency holdings and should never be shared. Store them securely and avoid saving them in easily accessible digital locations. Losing a private key can permanently restrict access to funds, while exposing it can allow unauthorized transactions. Treat private keys as highly sensitive financial information.

    Protect Your Recovery Phrase

    A recovery phrase can restore access to a cryptocurrency wallet, making its protection essential. Write the phrase down and store it somewhere secure and private. Avoid screenshots, cloud storage, emails or messaging apps. Never share recovery phrases with anyone claiming to provide wallet support or security assistance.

    Enable Multi-Factor Authentication

    Multi-factor authentication adds another layer of protection to cryptocurrency exchanges and related accounts. Whenever available, use an authenticator application or security key instead of relying exclusively on SMS. Strong authentication reduces the risk of account compromise, particularly if passwords are exposed through phishing attacks, data breaches or reused credentials.

    Create Strong, Unique Passwords

    Use long, unique passwords for cryptocurrency exchanges, wallets and associated email accounts. Avoid reusing passwords across multiple services because one compromised account can create additional security risks. A reputable password manager can help generate and store unique credentials, reducing the temptation to use predictable passwords or repeat the same password.

    Beware of Scams and Phishing

    Cryptocurrency users frequently encounter fake websites, investment schemes, impersonation attempts and phishing messages. Verify website addresses before entering credentials or approving transactions. Be particularly cautious about unexpected messages requesting payments, private keys or recovery phrases. Legitimate wallet providers and exchanges will not require users to reveal sensitive recovery information.

    Keep Software and Backups Updated

    Regularly update wallet applications, operating systems and security software to address known vulnerabilities. Maintain secure backups where appropriate and verify that recovery information remains accessible. For larger holdings, consider separating funds between wallets and keeping long-term assets offline. Security should combine technology, careful habits and protection against human error.

  • Top Identity Management Solutions for Enterprise Security and Access Control

    Top Identity Management Solutions for Enterprise Security and Access Control

    Identity management solutions are becoming essential as enterprises strengthen cybersecurity and manage digital access. Modern IAM platforms help organizations control user access while improving security and compliance.

    Single Sign-On (SSO) allows employees to access multiple applications with one secure login. Multi-Factor Authentication (MFA) adds another layer of protection beyond passwords. Role-based access control helps organizations assign permissions according to employee responsibilities.

    Cloud-based identity management platforms offer flexibility for hybrid and remote work environments. AI-powered identity security tools can detect unusual login activity and reduce cyber risks.

    Enterprises should evaluate scalability, integration options, compliance support, and pricing before choosing an IAM solution. The growing adoption of Zero Trust security is making identity management a key part of enterprise cybersecurity strategies.

  • Why Passwordless Authentication is a Game-Changer for Security

    Why Passwordless Authentication is a Game-Changer for Security

    Passwordless authentication is rapidly transforming how organizations protect digital identities. By eliminating traditional passwords, this approach addresses a wide range of security vulnerabilities while improving user experience. Below are the key benefits of adopting passwordless authentication.

    Eliminates Password Theft

    Traditional passwords are a prime target for cybercriminals. Passwordless authentication removes the risk of credential theft through phishing, brute-force attacks, password reuse, and database breaches. Without a password to steal, attackers lose a major entry point.

    Strengthens User Authentication

    Instead of relying on easily guessed or stolen passwords, passwordless methods use biometrics (fingerprint, facial recognition), security keys, or trusted devices. These factors provide a much higher level of assurance than conventional password-based systems.

    Reduces Phishing Attacks

    Phishing attacks often trick users into entering their passwords on fake websites. With passwordless authentication, users never enter a password, so attackers cannot steal credentials through deceptive login pages. This dramatically reduces the effectiveness of phishing campaigns.

    Improves User Experience

    Passwordless login simplifies access through fingerprint scans, facial recognition, passkeys, or device-based authentication. Users enjoy faster, frictionless logins without sacrificing security, leading to higher satisfaction and productivity.

    Minimizes Credential Reuse

    Many users reuse passwords across multiple accounts, increasing the risk of credential stuffing attacks. Passwordless authentication eliminates the practice of password reuse, reducing exposure when one service is compromised.

    Supports Multi-Factor Security

    Passwordless solutions can be combined with device verification, biometrics, or hardware tokens to create robust multi-factor authentication. This layered approach provides stronger protection against unauthorized access, even if one factor is compromised.

    Lowers IT Support Costs

    Organizations spend significant time and resources on password resets and account recovery. Passwordless authentication reduces help desk tickets related to forgotten passwords, freeing IT teams to focus on higher-value security initiatives.

    Enhances Regulatory Compliance

    Many regulations require strong authentication controls. Passwordless authentication helps organizations meet compliance standards for data protection and privacy, safeguarding sensitive business and customer information.

    Secures Remote Workforces

    As remote work becomes permanent, secure access to business applications is critical. Passwordless authentication allows employees to use trusted devices to log in from any location, maintaining security without compromising convenience.

    By adopting passwordless authentication, organizations can significantly improve their security posture while delivering a better user experience. The trend is clear: passwords are becoming obsolete, and passwordless authentication is the future of secure access.

  • Essential Zero Trust Security Practices Every Business Leader Should Implement

    Essential Zero Trust Security Practices Every Business Leader Should Implement

    In today’s evolving threat landscape, traditional perimeter-based security models are no longer sufficient. Business leaders must adopt a zero trust security approach that assumes no user, device, or network is inherently trustworthy. Below are the core practices that every organization should implement to strengthen their defenses.

    Verify Every User Continuously

    Authenticate every employee, contractor, and device on a continuous basis, rather than relying solely on network location or past authentication. This ensures that trust is never assumed and access is always verified.

    Enable Multi-Factor Authentication

    Strengthen login security by requiring additional identity verification factors. Multi-factor authentication dramatically reduces the risk of unauthorized access from stolen passwords or compromised credentials.

    Apply Least Privilege Access

    Grant employees only the permissions they need to perform their jobs. Limiting access to sensitive systems minimizes exposure and reduces the potential for insider or external cyberattacks.

    Segment Networks

    Divide your business infrastructure into isolated zones. Network segmentation prevents attackers from moving laterally after gaining access to a single system, containing breaches and limiting damage.

    Monitor User Activity

    Continuously analyze user behavior to detect suspicious actions, unusual login patterns, and potential security breaches early. Proactive monitoring helps stop attacks before significant harm occurs.

    Secure Endpoints

    Protect laptops, smartphones, servers, and all connected devices with endpoint detection, antivirus solutions, and regular software updates. Endpoint security is a critical layer in a zero trust architecture.

    Encrypt Sensitive Data

    Safeguard confidential information both at rest and in transit. Encryption ensures that even if data is intercepted, it remains unreadable without the proper decryption credentials.

    Automate Threat Detection

    Deploy AI-powered monitoring tools to identify vulnerabilities, suspicious activities, and emerging cyber threats faster than manual processes. Automation accelerates response times and reduces human error.

    Regularly Review Access Rights

    Audit employee permissions frequently, removing outdated accounts and unnecessary privileges. Regular reviews maintain strong cybersecurity hygiene and prevent privilege creep.

    By embedding these zero trust practices into your security strategy, you can better protect your organization from modern cyber threats and build a resilient defense posture.

  • Essential Data Security Practices for Remote Analytics Teams

    Essential Data Security Practices for Remote Analytics Teams

    Remote analytics teams handle some of the most valuable assets in modern organizations: customer information, operational metrics, financial records, and proprietary business intelligence. Effective data security requires multiple layers of protection, including access controls, encryption, endpoint security, and secure network connections.

    Why Is Data Security More Challenging for Remote Analytics Teams?

    Remote work has drastically altered the way companies use data analytics. Analysts have to work with various dashboards, cloud data warehouses, machine learning tools, customer databases, and other reporting systems from places outside of the conventional company network infrastructure.

    Such flexibility makes people more productive, yet, at the same time, it expands the area for potential attacks of hackers. People who conduct remote work might use public Wi-Fi, personal computers, their own routers, or even third-party apps to access the network.

    There is an increased risk for analysts, as they deal with a lot of confidential data. The hacking of such an analyst’s account might give hackers an opportunity to steal customer databases, financial reports, forecasts, or other important pieces of information.

    It is necessary to prevent such attacks not only because of the security, but also due to the necessity to comply with various privacy requirements and to guarantee the protection of data integrity.

    How Can Remote Teams Build a Secure Analytics Environment?

    A secure analytics environment relies on multiple protective measures working together. No single technology can eliminate all risks.

    1. Implement Strong Identity Controls

    Identity security comes first. Companies must have strong passwords, password managers, and multi-factor authentication (MFA). MFA decreases the probability of account hacking as hackers cannot get access without having access to more than just the password.

    There must also be role-based access controls where users will only have access to what is required in their roles.

    2. Encrypt Data in Transit and at Rest

    Encryption protects information from unauthorized viewing during transmission and storage. Cloud platforms, databases, analytics tools, and file-sharing systems should all use modern encryption standards. Teams should regularly verify that encryption settings remain enabled after software updates or platform migrations.

    3. Secure Network Connections

    Remote employees frequently connect from hotels, airports, cafes, coworking spaces, and home networks. Organizations should establish policies that require secure connections when accessing sensitive business systems.

    In some situations, teams may use secure VPN solutions to encrypt network traffic before accessing corporate resources. For example, in addition to additional security measures like MFA and endpoint protection, a free VPN service like Planet VPN can secure your connection. VPNs should be viewed as one component of a broader security framework rather than a complete solution.

    4. Protect Endpoints

    All laptops, workstations, and mobile devices used for analytics should be equipped with endpoint protection applications. Security professionals should make sure that the devices get OS updates and anti-malware protection without manual interventions. There are many device management tools which can facilitate the implementation of security policies.

    5. Monitor and Audit Access

    Continuous monitoring helps organizations identify unusual behavior before it becomes a serious incident. Security teams should review login patterns, access logs, permission changes, and data exports. Automated alerts can identify suspicious activities such as large downloads, unusual login locations, or repeated authentication failures.

    What Additional Security Layers Should Organizations Consider?

    Organizations that have advanced analytics systems may go further to employ defense-in-depth mechanisms for their cybersecurity needs.

    The Zero Trust system has gained popularity due to its assumption that nothing is to be trusted by default. All access requests are constantly checked and validated regardless of any location.

    The classification of data can also enhance security through recognizing which databases need extra measures of protection. Personal data of customers, financial data, data from the field of healthcare, and proprietary algorithms can need extra security measures compared to ordinary operation reports.

    Another useful mechanism is the data loss prevention system. The DLP system can help prevent any illegal dissemination of sensitive information.

    Security training of the staff is an essential measure. A significant number of successful attacks on businesses start from phishing attacks and human error and not from some technical flaws in the system.

    Periodic security assessment and testing are needed as well.

    What Common Data Security Mistakes Should Teams Avoid?

    A number of security breaches can be attributed to mistakes, rather than elaborate attacks.

    Excessive access rights represent one such common problem. Employees end up accessing various databases and systems even when their job responsibilities have changed. Such practices inevitably pose risks in the future.

    Another mistake involves the use of traditional security measures. With most employees working remotely and accessing company assets from different places, such security systems prove to be ineffective.

    Organizations tend to ignore the threats posed by shadow IT as well. Employees might start using unauthorized programs and productivity tools.

    Failing to patch the systems in time poses another vulnerability. Many attacks utilize existing flaws that could have been fixed already.

    The final common mistake includes concentrating too much on preventive measures and not on how to respond to the threat in case of an attack.

    What Are the Most Important Security Best Practices?

    Organizations can strengthen remote analytics security by following these core practices:

    • Require multi-factor authentication for all analytics and data platforms.
    • Limit user access according to business needs and job responsibilities.
    • Encrypt sensitive data during storage and transmission.
    • Maintain endpoint security across laptops, mobile devices, and workstations.
    • Monitor access logs and investigate suspicious activity quickly.
    • Conduct regular security awareness training programs.
    • Apply software updates and security patches without delay.
    • Develop and test incident response procedures regularly.
    • Classify sensitive data and apply stronger controls where necessary.
    • Review permissions and third-party integrations on a scheduled basis.

    These practices create multiple layers of protection that reduce risk while supporting productive remote collaboration.

    Frequently Asked Questions

    What are data security best practices for remote teams?

    Data security best practices for remote teams include multi-factor authentication, encrypted communications, endpoint protection, access controls, continuous monitoring, and employee security training. Organizations should combine multiple controls rather than relying on a single technology.

    Why is data security important for analytics teams?

    Analytics teams often work with highly sensitive information, including customer records, financial data, operational metrics, and strategic business intelligence. A security breach can expose valuable information and lead to compliance violations, financial losses, and reputational damage.

    How do remote employees protect sensitive business data?

    Remote employees can protect sensitive data by using strong authentication, secure devices, encrypted connections, approved software platforms, and company security policies. Regular software updates and awareness of phishing threats are also essential.

    Is a VPN enough to secure remote work?

    No. A VPN can help encrypt network traffic, but it does not replace identity management, endpoint protection, access controls, monitoring, or employee training. Effective security requires multiple layers working together.

    What is Zero Trust security?

    Zero Trust is a cybersecurity model that continuously verifies users and devices before granting access to resources. It assumes that no user, device, or network should be trusted automatically, even when operating inside a corporate environment.

    How often should organizations review data access permissions?

    Organizations should review permissions regularly, especially after role changes, employee departures, mergers, or major system updates. Quarterly reviews are common, although highly regulated industries may require more frequent assessments.