Blog

  • 7 Key Factors Behind EV Battery Range Loss: What Every Driver Should Know

    7 Key Factors Behind EV Battery Range Loss: What Every Driver Should Know

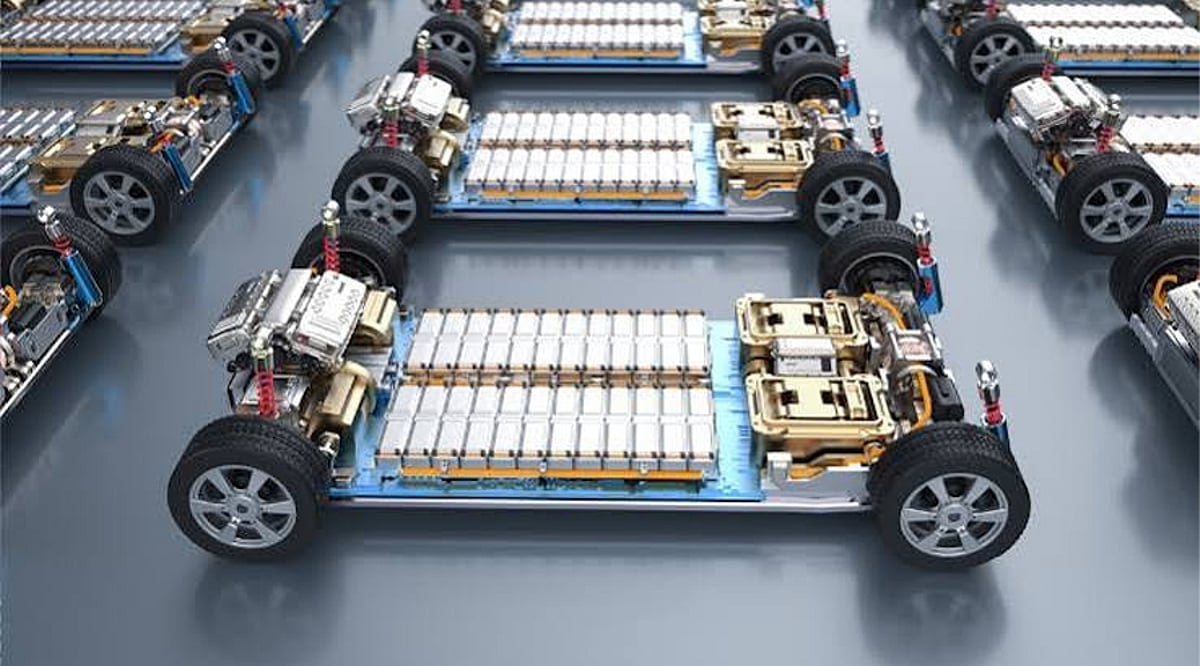
    Electric vehicle (EV) batteries gradually lose their ability to hold a charge, reducing driving range over time. Understanding the reasons behind this degradation can help drivers adopt habits that extend battery life. While many factors are at play, here are seven critical ones every EV owner should understand.

    1. Battery Chemistry and Natural Degradation

    Lithium-ion batteries undergo chemical and physical changes with repeated use, reducing their energy-storage capacity. The rate of degradation depends on battery chemistry, climate, charging habits, and thermal management systems.

    2. High Temperatures and Heat Exposure

    Extreme heat accelerates unwanted chemical reactions inside battery cells, leading to faster capacity loss. Modern EVs have thermal management systems, but prolonged exposure to high temperatures can still contribute to aging. Parking in shaded or cooler areas can help mitigate this effect.

    3. Frequent Fast Charging

    DC fast charging generates more heat and places greater stress on battery cells compared to slower charging. While convenient for quick top-ups, relying excessively on fast charging can hasten degradation. Balancing fast and regular charging promotes long-term battery health.

    4. Extended High or Low Charge Levels

    Keeping the battery at very high (near 100%) or very low (near 0%) charge for prolonged periods stresses the cells. Manufacturers typically recommend maintaining a charge between 20% and 80% for daily driving to reduce wear.

    5. Repeated Charging and Discharging Cycles

    Each full charge-discharge cycle causes small changes within battery cells. Over time, accumulated cycles reduce usable capacity. Driving patterns and charging frequency directly affect how many cycles a battery experiences.

    6. Battery Age and Calendar Aging

    Even when not used heavily, batteries chemically age naturally—a process known as calendar aging. This occurs alongside cycle-related degradation. Improved battery chemistry and management systems can slow these effects, but age remains an unavoidable factor.

    7. Driving Conditions and Energy Consumption

    Cold temperatures, high speeds, aggressive acceleration, heavy loads, hills, and extensive use of climate control increase energy consumption. These conditions can reduce real-world range without indicating permanent battery degradation.

    By understanding these factors, EV drivers can make informed choices about charging habits, driving style, and vehicle maintenance to maximize battery lifespan and range.

  • MEXC Launches Opportunity Compass to Bridge Crypto and Traditional Finance Knowledge Gaps

    MEXC Launches Opportunity Compass to Bridge Crypto and Traditional Finance Knowledge Gaps

    MEXC, a pioneer in zero-fee digital asset trading, has officially launched Opportunity Compass, a global markets education initiative designed to help crypto-native users better understand both digital and traditional financial markets. The program arrives as new research reveals that 53.7% of crypto users have already invested in stocks, yet significant knowledge gaps remain.

    Why Opportunity Compass Matters

    According to a joint survey by MEXC and CoinGecko, trading volumes for traditional financial assets on crypto exchanges hit $1.45 trillion in the first half of 2026—nearly ten times the total for all of 2025. The survey also found:

    • 53.7% of respondents have invested in stocks, indicating growing crossover between crypto and traditional markets.
    • Among those who haven’t used stock products, 43.1% cite insufficient investment knowledge as a key barrier.
    • Among former stock investors who stopped, 48.3% said limited knowledge contributed to their decision.
    • Current stock investors are influenced by individual stock price movements (44%) and the AI boom (34%).

    These findings underscore that access to financial products is expanding faster than financial literacy. MEXC’s Opportunity Compass aims to close that gap.

    A Five-Season Educational Journey

    The program features five seasons with 30 episodes, guiding users from foundational market knowledge to advanced opportunity evaluation:

    1. See the Global Opportunities – Understand the global financial landscape and how markets connect.
    2. Understand Asset Value – Explore what gives stocks, gold, commodities, ETFs, Bitcoin, and other assets their value.
    3. Decode Market Trends – Learn about interest rates, inflation, market cycles, earnings, and industry trends like AI and semiconductors.
    4. Explore Emerging Opportunities – Dive into tokenized assets, real-world assets, prediction markets, and other models at the intersection of crypto and traditional finance.
    5. Become an Opportunity Explorer – Build an independent framework for evaluating markets, opportunities, and risks.

    Content will roll out from September through December 2026 via a dedicated education hub.

    Industry Partnerships

    Opportunity Compass is not just an MEXC initiative—it brings together partners including xStocks by PAYWARD, Plume, Tether, Pyth, Optimism, CMT Digital, and RootData. These participants represent different parts of the digital asset and financial ecosystem, providing diverse perspectives.

    CEO’s Vision

    “Finding opportunities is important. What matters even more is having a systematic way to understand, evaluate, and act on them,” said Vugar Usi Zade, CEO of MEXC. “As financial markets become more connected, users need more than access alone. Opportunity Compass helps users understand what drives different markets, evaluate opportunities and risks, and build their own framework for navigating a more complex financial landscape.”

    All content is for educational purposes only and does not constitute financial or investment advice.

    About MEXC

    Founded in 2018, MEXC is a global multi-asset trading platform serving users across 170+ markets. It offers zero-fee trading for crypto, stocks, tokenized assets, derivatives, and TradFi-linked opportunities through a single account. MEXC is committed to making global opportunities more accessible.

  • Why Indian Smartphone Buyers Are Delaying Upgrades: Price Hikes, GST Uncertainty, and the Refurbished Shift

    Why Indian Smartphone Buyers Are Delaying Upgrades: Price Hikes, GST Uncertainty, and the Refurbished Shift

    Key Takeaways

    • Record-high smartphone prices are pushing budget-conscious buyers to postpone upgrades.
    • Refurbished phones are gaining traction as consumers seek better value.
    • Premium sales remain resilient through EMI financing, while affordable segments face steeper declines.

    India’s smartphone market is experiencing a pronounced slowdown as rising prices and economic uncertainty make buyers think twice before upgrading. According to Counterpoint Research, smartphone shipments fell 10% year-on-year in Q2 2026 — the steepest June-quarter decline in six years. IDC reports an even sharper 11.1% drop, with shipments totaling 33.2 million units. Both research firms point to the same underlying issue: consumers no longer see enough value in new phones at current prices.

    Higher Prices Have Changed the Buying Decision

    The average selling price of a smartphone in India reached a record $315, according to IDC, a 14.4% increase over the previous year. Counterpoint estimates that phone prices climbed roughly 15% by the end of Q2 2026, driven by multiple price hikes across major brands. This surge hits the mass market hardest, where even a modest price increase can push a purchase beyond a household’s budget.

    Memory costs are at the heart of the problem. Smartphone memory prices have nearly quadrupled since September 2025, Counterpoint notes, and now account for more than 45% of the bill of materials for phones priced below ₹15,000 — up from less than 20% before. Some models have seen price increases of over 100% from their launch price.

    The impact on price-sensitive buyers has been severe. Shipments of phones in the sub-₹15,000 segment fell 45% year-on-year in Q2. IDC also recorded a 74.3% drop in phones priced below $100. These figures demonstrate how quickly rising component costs can alter consumer behavior at the entry level.

    Buyers Can Get More Value From Older Phones

    A new phone no longer offers the same clear value at the lower end. Consumers can keep their current handset for another year rather than pay more for only modest improvements. Longer replacement cycles have become a key market dynamic, according to Counterpoint.

    The refurbished market provides strong evidence of this shift. India’s refurbished smartphone market grew 13% in the first half of 2026, while new phone sales fell about 11%. Refurbished devices often offer better cameras, displays, and processors at a lower price than comparable new models. Counterpoint expects the refurbished market to grow 16% in 2026.

    This trend also underscores that demand for smartphones hasn’t disappeared. Consumers still want better devices, but price has become a stronger determining factor. A used premium phone now looks more attractive than a new budget handset, especially for buyers focused on camera quality, display performance, and processor speed.

    GST Uncertainty Gives Buyers Another Reason to Wait

    Tax policy adds another layer of hesitation. Smartphones currently carry an 18% Goods and Services Tax (GST). Reports have suggested possible cuts to 12% or even 5%, though no reduction has been confirmed.

    The next GST Council meeting has been rescheduled to October 7, 2026, from the earlier September 12 date. This change gives buyers another reason to postpone a purchase until there is greater clarity on smartphone taxes.

    A lower GST rate could create a meaningful difference at retail. On a phone priced at ₹15,000 before tax, moving from 18% GST to 12% would reduce the tax component by about ₹676. A move to 5% would cut it by roughly ₹1,950, assuming retailers pass the full benefit to buyers. Actual retail savings may vary.

    EMI Plans Keep Premium Phones Strong

    The slowdown does not affect every market segment equally. Premium phones continue to attract buyers, thanks in part to EMI financing that reduces upfront costs. More than half of mainline smartphone sales used some form of financing in Q2, according to Counterpoint. The average EMI tenure reached 10 months, with Apple having the highest average at 17.2 months.

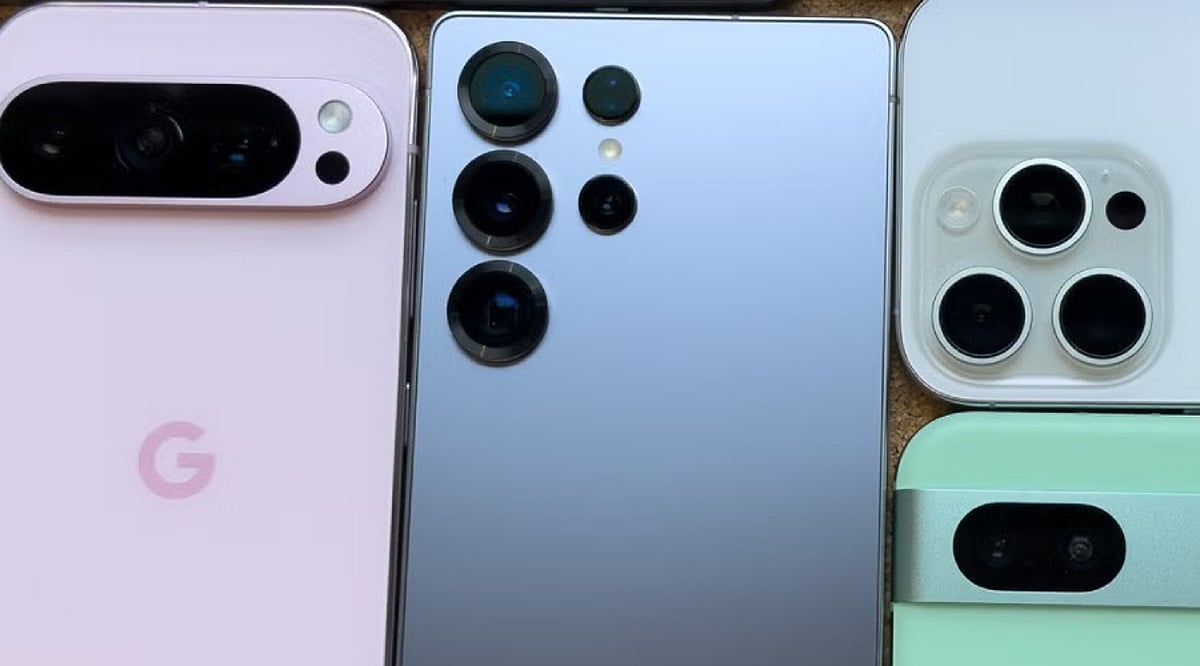
    Google Pixel posted 68% year-on-year growth in the ultra-premium segment above ₹45,000. Samsung grew 2% among the top five brands, while Nothing posted 105% growth. These results reveal a market split between buyers who can stretch budgets for premium devices and those who must delay purchases.

    The Wait Could Make Phones Costlier

    The biggest tension lies between hopes for a GST cut and rising component costs. A buyer may wait for a possible tax reduction, yet memory prices may push phone prices higher before any relief arrives. Counterpoint expects memory prices to rise further, possibly to five times their September 2025 level, and forecasts a 13% decline for India’s smartphone market across 2026.

    India’s smartphone slowdown looks less like a loss of interest and more like a value problem. Buyers still want better phones, but higher prices have shifted the point at which a replacement makes financial sense. For mass-market consumers, the choice now often boils down to three options: keep the old phone, buy refurbished, or wait for a price cut. That shift could keep India’s smartphone market under pressure well beyond a single sales quarter.

  • XRP Ledger Liquidity Surges 79% as Institutional-Scale Trades Outpace Account Growth

    XRP Ledger Liquidity Surges 79% as Institutional-Scale Trades Outpace Account Growth

    XRP Ledger (XRPL) produced an unusual combination of market data during Q2 2026: fewer accounts were trading, yet substantially more XRP moved through its order book. The divergence highlights why raw wallet or active-account figures can provide an incomplete picture of blockchain adoption, particularly when larger and potentially more professional trades become more important.

    XRPL Order-Book Volume Increased 79%

    According to Evernorth’s Q2 2026 XRP Liquidity Report, XRP Ledger order-book trading averaged 3.57 million XRP per day, up 79% from approximately 1.99 million XRP a year earlier. Participation moved in the opposite direction. Daily accounts initiating order-book trades fell approximately 40%, from 1,864 to 1,111.

    That pushed average trading activity per participating account from 1,072 XRP per day to 3,217 XRP, roughly three times the year-earlier level. Order books also accounted for 81% of XRPL decentralized exchange activity, compared with 54% one year earlier.

    Bigger Accounts Do Not Automatically Mean Institutions

    The data is consistent with larger or more professional traders becoming more active, but it does not prove that institutions are responsible for the increase. One institution can operate multiple blockchain accounts, while one individual can control several addresses. Account numbers, therefore, cannot be directly translated into the number of traders.

    What the data does establish is greater concentration: fewer accounts are moving considerably more XRP. That matters for liquidity because larger traders typically care about whether significant orders can execute with limited slippage, not simply how many wallets are active.

    Tokenized Value Is Also Growing

    The broader XRPL data strengthens the case that economically larger activity is developing on the network. Tokenized assets averaged approximately USD 3.72 billion during Q2, more than 30 times their level a year earlier. Average Ripple USD balances reached USD 539 million, up from USD 73 million, while total value held on XRPL averaged approximately USD 4.26 billion.

    RLUSD’s share of its total supply held on XRP Ledger also increased from 20% to 34%, while transferred RLUSD value rose 925% year over year.

    Lending Could Put That Liquidity to Work

    The next development to watch is native credit infrastructure. XLS-65 and XLS-66 are designed to combine Single Asset Vaults with fixed-term, underwritten lending facilities. XRPL Commons described the model in September as moving XRPL from settlement toward a native institutional credit layer, potentially allowing tokenized assets and stablecoin liquidity to be deployed rather than simply held or traded.

    That makes liquidity quality increasingly important. A lending market needs sufficient depth to enter positions, price collateral and liquidate assets efficiently when borrowers default.

    Liquidity Matters More Than Transaction Counts

    A blockchain can have millions of users but still be unsuitable for institutional settlement if executing a USD 10 million transaction materially moves the market. Conversely, fewer participants can support significant financial activity when order books provide sufficient depth and reliable execution.

    Why This Matters

    XRPL’s falling trader count does not necessarily signal weaker adoption. Rising volume per account, growing tokenized assets and expanding RLUSD liquidity suggest that the economic size of activity may matter more than the number of participating wallets.

    Final Thoughts

    XRPL’s next growth phase will depend on whether larger trading volumes translate into deeper, more resilient liquidity. If vaults and lending expand, order-book depth, spreads and stablecoin liquidity will become increasingly important indicators of institutional readiness.

  • Essential Cybersecurity Lessons from the Growing Use of AI Agents

    Essential Cybersecurity Lessons from the Growing Use of AI Agents

    As artificial intelligence agents become more capable and autonomous, they are increasingly handling sensitive tasks across business systems. While this brings efficiency, it also introduces new cybersecurity challenges. Here are the key lessons organizations must learn to protect their AI-driven operations.

    Strong Access Controls

    AI agents often require access to files, applications, and systems to complete their tasks. Limiting these permissions helps reduce potential damage if an agent behaves unexpectedly or its credentials are compromised. Implement the principle of least privilege.

    Protect Sensitive Data

    AI agents may handle customer information, business records, and confidential documents. Organizations should restrict sensitive data access and apply strong encryption, authentication, and privacy controls to safeguard this information.

    Continuous Monitoring

    Because AI agents can perform tasks independently and at high speed, continuous monitoring is essential. Security teams need to identify unusual activity, unexpected decisions, and potential attacks before they escalate.

    Human Oversight Matters

    Autonomous systems should not operate without appropriate human checks. Critical actions involving finances, sensitive information, or important infrastructure should require human approval before completion.

    Secure Agent Communication

    AI agents often interact with applications, APIs, databases, and other agents. Securing these connections helps prevent attackers from intercepting instructions or manipulating exchanged information.

    Test Before Deployment

    Organizations should test AI agents against malicious prompts, incorrect instructions, data leaks, and unexpected behaviors. Regular security testing can reveal weaknesses before agents are deployed widely.

    Prepare for New Threats

    The growth of AI agents creates new attack possibilities, including prompt manipulation, privilege abuse, and automated attacks. Security teams need updated policies and response plans to manage these evolving risks.

  • Kaspersky Launches App Cleaner for macOS to Remove Hidden App Leftovers

    Kaspersky Launches App Cleaner for macOS to Remove Hidden App Leftovers

    Kaspersky has introduced a new feature called App Cleaner as part of Kaspersky Premium for macOS, designed to tackle a persistent issue for Mac users: leftover files that remain even after applications are uninstalled. When users drag an app to the Trash, caches, preferences, support files, and other associated data often stay behind, gradually consuming disk space and contributing to digital clutter. App Cleaner ensures complete removal of apps without leaving traces, and also detects and deletes leftover files from previously uninstalled applications.

    The Hidden Cost of Uninstalling Apps

    A recent Kaspersky survey revealed that macOS users are generally proactive about managing digital clutter. Nearly 56% clear browser history, cookies, cache, and temporary files, while 54% manage or delete unnecessary files like photos and videos. However, only 44% regularly delete unused or rarely used apps. Removing leftover files from uninstalled apps remains an overlooked challenge.

    When an app is deleted by dragging it to the Trash, users often assume it is completely gone. In reality, settings, caches, logs, support files, and other associated data may persist on the disk. These leftovers can be difficult to locate and, in some cases, occupy more space than the original application—especially for browsers. Some app components may also be hidden from the standard macOS interface, making them hard to detect.

    Leftover files may contain sensitive information, including account tokens, saved passwords, activity logs, IP addresses, usernames, document fragments, images, chats, and personal folder paths. If an attacker gains access to the device, or if it is sold or given away without being fully wiped, these files could be used to recover passwords, steal personal data, or access user accounts.

    How App Cleaner Works

    App Cleaner solves this problem by detecting and deleting associated files when a user removes an app. It can also find and remove leftover app-specific files from applications that were uninstalled in the past. The exception is shared files—App Cleaner will not delete files used by other apps, such as common components shared between Microsoft Office apps. These files can only be deleted along with the last application that uses them.

    Security Beyond Cleanup

    While macOS has long been considered more secure, today’s threats are not limited to viruses. Ransomware, trojans, spyware, online scams, phishing credential theft, and other threats pose risks to Mac users. Kaspersky specialists have even identified cases where malware was disguised as legitimate cleaning software, impersonating tools like CleanMyMac, Mole, or CCleaner Pro. The company warns users to stay vigilant when downloading any cleaning software, especially from third-party websites.

    Irina Ermilova, Vice President for Consumer Product Management at Kaspersky, commented: “We’ve seen growing demand for device management tools as users accumulate more digital content. Yet a patchwork of third‑party utilities is both inconvenient and risky. With App Cleaner, macOS users can clean up digital leftovers without installing additional software – keeping their devices secure and clutter‑free.”

    Essential Security Practices for Mac Users

    Beyond using App Cleaner, Kaspersky experts recommend the following practices to keep Mac devices secure:

    • Use a dedicated security solution. While macOS has built‑in protections, security software adds a crucial layer of real‑time defense against threats that the system alone cannot block. Kaspersky Premium for macOS protects against ransomware, trojans, spyware, phishing, and hacking attacks.
    • Grant necessary permissions. For any security software to function properly, it needs full disk access and the ability to install system extensions and network content filtering. Without these permissions, protection features may not work as intended.
    • Keep apps and OS updated. Regular updates include critical security patches and new features.
    • Be cautious with downloads and links. Phishing attacks rely on social engineering and can appear in emails, messages, or websites. Avoid opening suspicious links or downloading unverified software.
    • Remove sensitive data before handing over your Mac. If you lend or transfer your device, remove sensitive files and sign out of personal accounts. Before selling or giving away your Mac, perform a complete factory reset.

    The survey was conducted by Kaspersky’s market research center in March 2026, with 7,200 respondents from 18 countries.

    Kaspersky is a global cybersecurity and digital privacy company founded in 1997. It protects over a billion devices and serves consumers, businesses, critical infrastructure, and governments worldwide.

  • France’s E-Invoicing Mandate: Is Your Business Ready for the 2026 Deadline?

    France’s E-Invoicing Mandate: Is Your Business Ready for the 2026 Deadline?

    The digitalization of tax administration is accelerating globally, and Europe is at the forefront. France’s Ministry of Economy, Finance, and Digital Sovereignty is implementing a groundbreaking digital tax reform that will fundamentally change how businesses handle invoicing and reporting. If your company operates in France, trades with French companies, or is subject to French VAT, understanding these new obligations is critical.

    The reform has two main components: mandatory electronic invoicing for domestic B2B transactions and mandatory e-reporting for cross-border, B2C, and overseas activities. Companies must adapt their ERP and accounting processes well before the implementation deadlines.

    Understanding the Core Architecture of France’s E-Invoicing Reform

    The French mandate rests on two pillars: mandatory electronic invoicing and dynamic e-reporting. The French tax administration (Direction Générale des Finances Publiques – DGFiP) aims to deter VAT fraud, reduce administrative burdens, and gain real-time access to economic activity.

    Unlike traditional paper or unstructured PDF invoices sent via email, e-invoicing under the new framework requires structured digital formats that enable automated machine processing. Invoices will no longer be sent directly from supplier to buyer; they must pass through validated digital channels that extract key tax data and transmit it to a national central hub.

    1. Electronic Invoicing (E-Invoicing)

    Mandatory e-invoicing targets all domestic Business-to-Business (B2B) transactions between companies established in France. Every tax-registered company must be capable of receiving structured electronic invoices, and sellers must issue them in standardized formats such as UBL 2.1, CII (Cross Industry Invoice), or Factur-X (a hybrid format combining a human-readable PDF with embedded XML data).

    2. Electronic Reporting (E-Reporting)

    Transactions outside domestic B2B scope are governed by e-reporting rules. This includes:

    • Business-to-Consumer (B2C) Transactions: Domestic and international sales to end consumers.
    • Cross-Border B2B Transactions: Intra-EU acquisitions, cross-border sales, and international import/export activities.
    • Payment Status Data: For services, payment date status must be reported to enable accurate VAT collection on an accrual or cash-received basis.

    The Regulatory Timeline: Phased Implementation Schedule

    The French government has established a phased implementation roadmap to allow businesses to progressively integrate necessary software and test data flows. While mandatory issuance is tiered by company size, every business in France must be equipped to receive structured e-invoices starting in September 2026. Waiting until 2027 is risky even for smaller enterprises, as receipt capability demands functional integration, system updates, and employee training today.

    Technical Infrastructure: PDP, PPF, and OD

    The operational framework relies on a Y-shaped architectural ecosystem designed by the French tax authority:

    • Public Billing Portal (Portail Public de Facturation – PPF): The state-run central repository that aggregates transaction data for tax oversight, provides basic free invoicing services, and routes data directly to the tax authority.
    • Partner Dematerialization Platforms (Plateformes de Dématérialisation Partenaire – PDP): Third-party certified service providers that convert non-compliant formats, validate invoice integrity, exchange invoices between platforms, and automatically route tax data to the PPF.
    • Dematerialization Operators (Opérateurs de Dématérialisation – OD): Uncertified technology vendors that can generate or process electronic invoices but cannot connect directly to the PPF or other PDPs without relying on an accredited PDP or manual intervention.

    Key Compliance Takeaway: For multinational businesses with complex ERP ecosystems like SAP, Microsoft Dynamics, or Oracle, partner integration with an accredited PDP is essential to automate high-volume invoice routing, schema transformation, and status tracking without breaking existing business logic.

    Operational Challenges and How to Prepare Your Business

    Transitioning to full compliance requires more than installing a simple software plugin. It impacts core finance, procurement, tax governance, and IT infrastructure. Organizations should undertake a systematic implementation strategy focused on:

    1. Data Governance and Master Data Cleanup

    E-invoicing validation engines rigorously inspect mandatory fields. Errors in SIREN, SIRET, or intra-community VAT numbers, customer addresses, or incorrect tax classification codes will cause instant invoice rejection. Establishing robust master data governance is step one.

    2. ERP and Financial System Alignment

    Assess your current ERP stack. Does your billing system support structured formats such as Factur-X or UBL? Does it track mandatory invoice lifecycle statuses (e.g., Deposited, Approved, Refused, Received, Payment Complete)? ERP systems must be configured to process real-time status feedback loops.

    3. Cross-Border Tax Strategy

    Ensure your tax technology stack can differentiate between domestic B2B flows (requiring e-invoicing) and cross-border or B2C flows (requiring structured e-reporting). Misclassifying transactions will result in compliance gaps and potential tax penalties.

    Future-Proofing Compliance with Integrated Solutions

    Given the shift toward real-time transaction management, maintaining separate systems for each country is unsustainable. Enterprises need scalable solutions that integrate easily with existing ERP environments. SNI Technology offers comprehensive, fully automated solutions for SAP-based compliance, helping businesses meet French e-invoicing and e-reporting requirements through automation of invoice creation, format transformation, validation, and routing via certified PDP channels.

  • Wipro and CrowdStrike Launch CISO Command Center to Transform Enterprise Cybersecurity with AI-Driven Risk Management

    Wipro and CrowdStrike Launch CISO Command Center to Transform Enterprise Cybersecurity with AI-Driven Risk Management

    EAST BRUNSWICK, NJ | BENGALURU, India | AUSTIN, Texas – Wipro Limited (NYSE: WIT, BSE: 507685, NSE: WIPRO), a leading AI-powered technology services and consulting company, today announced the launch of its Chief Information Security Officer (CISO) Command Center, in collaboration with CrowdStrike (NASDAQ: CRWD). The Command Center rewires enterprise security for frontier AI-accelerated risks to create proactive, risk-informed cyber resilience aligned to business priorities.

    The CISO Command Center reinforces Wipro’s consulting-led cybersecurity strategy by enabling enterprises to move from tool-driven operations to an enterprise-wide, risk-led operating model. The Center will be operationalized through Wipro Intelligence™ solutions – CyberTransformSM and CyberShieldSM – and supported by the CrowdStrike Falcon® platform. It will deliver integrated protection across endpoint security, cloud security, exposure management, and AI security, while unifying detection and response through a modern Security Operations Center (SOC).

    “Cyber risk is intensifying pressure on boardroom decision-making. Threats that once remained dormant for months can now materialize within hours, driven by external triggers and AI-enabled exploitation,” said Amar Bysani, Global Practice Head – Cybersecurity and Risk Services, Wipro Limited. “The Command Center will work with enterprises to turn security signals into business risk intelligence, enabling them to sense, prioritize, and respond at machine speed.”

    Daniel Bernard, Chief Business Officer, CrowdStrike, said: “AI is fundamentally changing both the threat landscape and how enterprises run defense programs. Together, CrowdStrike and Wipro are giving CISOs the AI-native security, intelligence, and services they need to turn risk into action at machine speed and transform security into a business advantage.”

    The offering is further strengthened by Wipro’s membership in CrowdStrike’s Project QuiltWorks, a global coalition focused on identifying, prioritizing, and remediating frontier AI risk.

    About Wipro Limited
    Wipro Limited (NYSE: WIT, BSE: 507685, NSE: WIPRO) is a leading AI-powered technology services and consulting company focused on building innovative solutions that address clients’ most complex digital transformation needs. Leveraging a consulting-led approach and the Wipro Intelligence™ unified suite of AI-powered platforms, solutions and transformative offerings, the company helps clients realize their boldest ambitions to build intelligent and sustainable businesses. With over 240,000 employees and business partners across 65 countries, Wipro delivers on the promise of helping customers, colleagues, and communities thrive in an ever-changing world. For additional information, visit www.wipro.com.

    About CrowdStrike
    CrowdStrike (NASDAQ: CRWD), a global cybersecurity leader, has redefined modern security with the world’s most advanced cloud-native platform for protecting critical areas of enterprise risk – endpoints and cloud workloads, identity and data. Powered by the CrowdStrike Security Cloud and world-class AI, the CrowdStrike Falcon® platform leverages real-time indicators of attack, threat intelligence, evolving adversary tradecraft, and enriched telemetry from across the enterprise to deliver hyper-accurate detections, automated protection and remediation, elite threat hunting, and prioritized observability of vulnerabilities. Learn more at www.crowdstrike.com.

  • SpyCloud Report: Non-Hhuman Identities Emerge as Leading Enterprise Attack Vector

    SpyCloud Report: Non-Hhuman Identities Emerge as Leading Enterprise Attack Vector

    Survey Reveals Critical Gap Between Perceived and Actual Visibility into Machine Identities

    SpyCloud, a leader in identity threat protection, has released its annual 2026 Identity Threat Report, revealing that non-human identities (NHIs) — including AI agents, service accounts, API keys, and authentication tokens — have become the most common initial attack vector into enterprise systems. The report, based on a survey of 750 cybersecurity leaders and practitioners across North America, the UK, and select European markets, underscores a dangerous disconnect: while 95% of organizations believe they have adequate visibility into AI- and NHI-related exposures, only 36% actually monitor these identities.

    Key Findings: NHIs Outpace Phishing as Top Entry Point

    The survey found that compromised NHIs were the primary entry point for attacks in 31% of cases — nearly double the rate of phishing and social engineering (17%), which ranked second. NHI-related misuse also surfaced as the most common identity-based event type, reported by 42% of organizations. Yet, despite this prevalence, machine identities remain the least-monitored category of identity risk. In the same period, 68% of organizations experienced at least one identity-based event, with affected organizations averaging eight incidents each.

    Organizations typically maintain clear inventories of their human workforce, but few extend that oversight to service accounts, API keys, and AI agents. These identities are often provisioned for convenience, hold substantial privilege, and lack the lifecycle management that human accounts have. As Trevor Hilligoss, SpyCloud’s Chief Intelligence Officer, noted: “Every one of these identities is a standing invitation that renews itself until someone notices.”

    AI Adoption Outpaces Governance

    While 91% of organizations now use AI tools or agents with access to internal systems, only 56% have formal governance and ownership for the privileges these identities hold. Another 41% rely on informal processes or partial ownership, creating “shadow access” — privileged connections that operate outside normal governance and monitoring.

    Session Hijacking and Stolen Cookies Pose Growing Risk

    The report highlights that exposed session cookies and authentication tokens are becoming a preferred attack vector, allowing cybercriminals to bypass multi-factor authentication (MFA). Organizations with visibility into stolen session data experienced identity-based events at a meaningfully lower rate (37%) compared to those without such visibility (50%). SpyCloud research confirms that session data has now overtaken passwords as the top target for attackers.

    Supply Chain Vulnerabilities Remain a Concern

    Third-party exposures are also a major concern. Malware-infected third-party devices (23%) and exposed API keys or application access involving vendors (22%) were the leading causes of supply chain identity events. Surprisingly, nearly 40% of organizations have no consistent process to confirm that third-party exposures are fully resolved, even as 32% plan to enhance supply chain and vendor risk management in the next 12 to 18 months.

    Automation and Continuous Monitoring Are Key Differentiators

    The report introduces SpyCloud’s Identity Threat Protection Maturity Model, categorizing organizations into four tiers: Reactive, Building, Operational, and Optimized. Findings show that organizations with high levels of automation report lower incident response costs (32% vs. 39%) and less loss of customer trust (36% vs. 47%) compared to those relying on manual remediation.

    “Most identity programs are still measured on whether an exposure happened. That’s the wrong scoreboard,” said Damon Fleury, Chief Product Officer at SpyCloud. “Organizations that pair continuous identity monitoring with automated remediation create the greatest friction for criminals and gain the biggest edge in preventing follow-on attacks.”

    About the Report

    The full 2026 SpyCloud Identity Threat Report is available without registration, and organizations can benchmark their security posture against the maturity model via a free assessment. SpyCloud, headquartered in Austin, TX, serves 7 of the Fortune 10 and hundreds of global enterprises, mid-sized companies, and government agencies.

    This is a paid press release published via CyberNewswire, a PR newswire syndication platform for cybersecurity companies.

  • How Naol Bassaye’s Seeft Brings Enterprise-Grade Process Intelligence to Mid-Sized Businesses

    How Naol Bassaye’s Seeft Brings Enterprise-Grade Process Intelligence to Mid-Sized Businesses

    For years, advanced process-intelligence tools have been reserved for the world’s largest companies—organizations that can afford complex deployments, external consultants, and dedicated teams to manage lengthy implementation cycles. Meanwhile, many mid-market businesses face similar operational challenges but lack the resources to adopt the same technology.

    Naol Mekuriya Bassaye saw this divide firsthand during his two years at Celonis, where he developed process-intelligence solutions for multinational enterprises across energy, aviation, automotive, pharmaceuticals, medical devices, and industrial manufacturing. His work gave him an inside look at how large companies use operational data to trace activity, locate inefficiencies, and improve cross-department workflows—and it also revealed how many businesses remained locked out of that system.

    “Complexity does not begin at the Fortune 500 level, but access to the best tools often does,” said Bassaye. “A mid-sized manufacturer can face demanding operational problems without the budget, implementation support, or internal resources available to a global enterprise.”

    Now, as co-founder and chief technology officer of Seeft, Bassaye is adapting enterprise-grade process intelligence for mid-sized businesses that make, move, and sell physical goods. His approach goes beyond simply lowering the price of a large-company platform; he believes mid-market businesses need a fundamentally different product philosophy.

    “A smaller company does not need a diluted enterprise system,” he explained. “It needs software built around its own operating reality. The setup has to be faster, the value has to arrive sooner, and the product cannot assume there is a large transformation team waiting to manage it.”

    Seeft is entering the market through the procure-to-pay workflow—a process that crosses several departments and offers a contained opportunity to prove the value of a broader operational system. Instead of requiring a drawn-out technology program, the goal is to help a company identify meaningful opportunities within one to two weeks.

    Bassaye sees speed as a critical component of accessibility. A lower subscription price offers little benefit if a business must still spend months preparing data, coordinating consultants, and assigning employees to support implementation.

    “Time is one of the costs people forget to measure,” he said. “A product can look affordable on paper and still be unrealistic once you account for the people and effort required to make it useful.”

    His perspective has been shaped by experiences beyond Celonis. As former CTO of an aerospace workflow-optimization company, Bassaye learned firsthand how weak implementation can have serious consequences. In one case, a problem remained unresolved after nearly two months of remote discussions. He visited the site, spent three days observing work directly, and compressed the investigation into that shorter period.

    “The issue became clearer once I could see the environment and watch the handoffs,” he recalled. “People often describe a process based on how it is supposed to function. The product has to account for how the work is actually completed.”

    That lesson now shapes his approach to mid-market customers. Software built for operational teams must reflect workarounds, informal decisions, and practical constraints that rarely appear in a formal process map.

    Bassaye also brings experience building products outside traditional enterprise engagements. He created a synthetic data generator used by more than 10,000 people, producing over 2 billion data points. The project pushed him to consider adoption, usability, and scale beyond technical architecture.

    “Building something technically sound is only one part of the job,” he said. “A product has to make sense to the person using it. If the value requires constant explanation, the design is probably asking too much from the customer.”

    His work has attracted attention from selective startup programs. Three Sigma, his previous company, was accepted into Antler’s UK Spring cohort (with an acceptance rate below 2%) and later included in a £1.7 million investment round covering 14 businesses chosen from over 5,000 applicants. Bassaye has since received backing for Seeft through Entrepreneur First.

    “A customer does not care that a product was selected by a respected program,” he noted. “They care whether their team can adopt it without reorganizing the entire company.”

    That standard has become increasingly relevant as artificial intelligence lowers the cost of building advanced software. Capabilities that once required extensive custom development can now be delivered more efficiently, but Bassaye cautions that easier development does not automatically produce a useful operational tool. Mid-market companies still need technology that respects their staffing limits, protects critical workflows, and reaches meaningful results without forcing an enterprise-scale implementation model.

    “The opportunity is larger than making old software cheaper,” Bassaye said. “AI gives us the chance to redesign the category around companies that were never well served by it in the first place.”

    Seeft’s initial focus is procurement, but Bassaye plans to extend the same approach into collections, inventory, and fulfillment—each area affecting working capital and requiring coordination across multiple functions. The larger ambition is to reduce the operational advantage that has traditionally come with size. A global corporation may always have more resources, but Bassaye believes sophisticated visibility should no longer depend entirely on budget or headcount.

    Leaders in these companies—often a COO or CFO of a firm large enough to have real process complexity but small enough that they still carry most of it themselves—rarely lack judgment about their own business. What they lack is the staff to assemble the picture that judgment depends on: the week of analyst time that turns scattered ERP records into a ranked list of what is actually costing money. Software that does that assembly doesn’t replace the decision; it moves the operator from reconstructing what happened to deciding what to do about it, and it shortens the distance between noticing a problem and acting on it.

    “Good operational judgment begins with having a clear view of the work,” Bassaye concluded. “Mid-market leaders should not have to operate with less clarity simply because enterprise technology was not built for them.”