Tag: AI Governance

  • U.S. and China Reach Tariff Framework and Launch First AI Dialogue

    U.S. and China Reach Tariff Framework and Launch First AI Dialogue

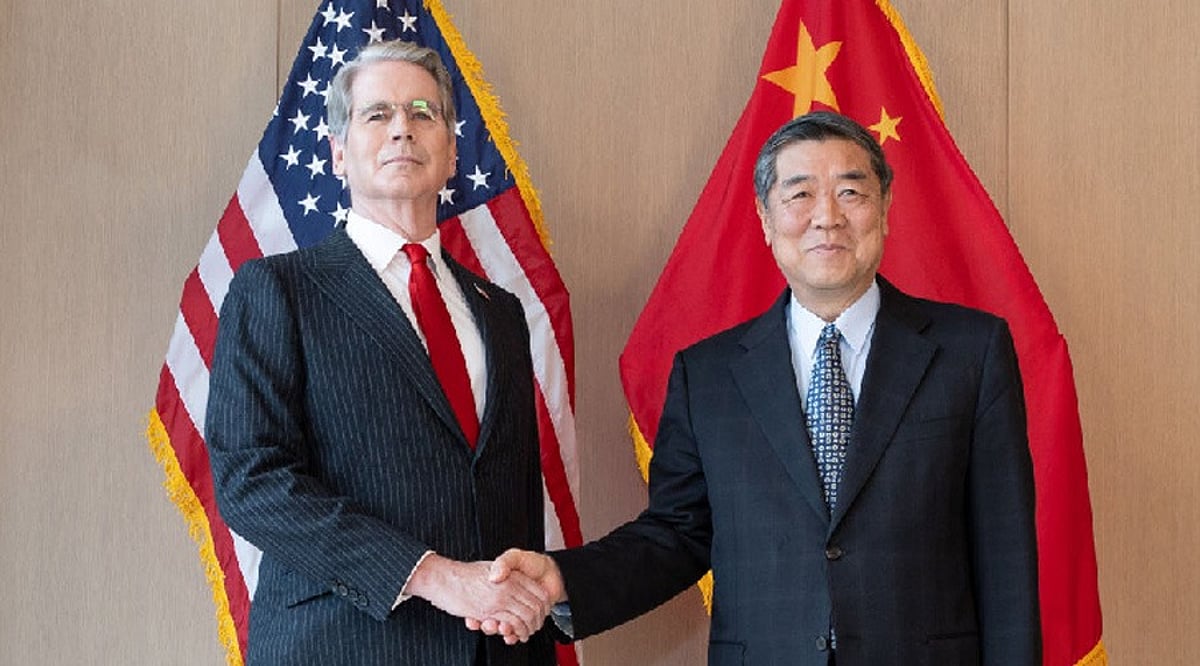
    China and the United States have reached agreement on several economic and trade issues after their latest consultations in New York, China’s Ministry of Commerce said. The talks produced a proposed reciprocal tariff reduction and opened the first formal bilateral dialogue on artificial intelligence under the two countries’ economic and trade consultation framework.

    Tariff framework targets USD 30 billion in goods on each side

    The proposed framework would lower tariffs on selected products worth USD 30 billion on each side. China’s commerce ministry had previously indicated that the two governments were working toward an arrangement covering goods of equivalent value. The plan is intended to ease trade barriers between the world’s two largest economies, but it is not an immediate, across-the-board tariff cut. Specific products and implementation steps remain under negotiation, and the ministry said it would provide further updates as work progresses.

    New trade and investment councils proposed

    Beyond tariffs, the discussions covered implementation of existing agreements and the creation of trade and investment councils. Those bodies would give both sides a regular mechanism for addressing economic concerns and reviewing earlier arrangements.

    First AI dialogue brings technology governance into trade talks

    Chinese Vice-Premier He Lifeng and U.S. Treasury Secretary Scott Bessent, who lead their countries’ economic teams, held the first AI dialogue under the economic and trade consultation mechanism. The two governments had already agreed to establish an intergovernmental dialogue on AI, with earlier discussions covering technological risks and global AI governance. AI has become a central part of the broader relationship as the two countries compete in advanced technology and weigh the risks of increasingly capable systems.

    Trade tensions remain unresolved

    The consensus marks another step in managing a complex relationship rather than a full resolution of outstanding disputes. Tariffs, trade barriers, and other economic issues remain on the agenda, and earlier arrangements are being extended or reviewed. Both sides are expected to continue talks through existing consultation channels.

    For businesses, the proposed tariff reductions could eventually bring more clarity on selected product categories if the framework moves into implementation. The formal AI dialogue also gives Beijing and Washington an additional channel to discuss technology risks, governance, and wider implications.

  • Understanding AI Guardrails: Why Enterprises Need Them for Safe and Compliant AI Deployment

    Understanding AI Guardrails: Why Enterprises Need Them for Safe and Compliant AI Deployment

    As enterprises rapidly integrate artificial intelligence into customer support, coding, analytics, and daily operations, the speed of adoption brings significant risks. A single erroneous response or data leak can undermine trust and profitability. This is where AI guardrails become essential. Acting as safety barriers, they keep AI systems within defined boundaries, ensuring safety, accuracy, and compliance.

    What Are AI Guardrails?

    AI guardrails are rules, filters, and checks that control what an AI system can receive as input and what it can generate as output. They operate in real-time, intercepting unsafe content before it reaches users. Some guardrails screen prompts, while others inspect responses. A robust setup also logs every decision for audit trails. These tools can prevent prompt attacks, redact personal data, and flag fabricated information.

    Risks Addressed by AI Guardrails

    Generative AI introduces real risks: incorrect or biased answers, privacy breaches, jailbreak attempts, and misuse. Prompt injection, where hidden text tricks a model into ignoring its rules, is a primary attack vector. According to the Stanford AI Index, documented AI incidents surged by 56.4% in a single year. These risks impact security, legal compliance, and brand reputation. The stakes are even higher with AI agents, which can execute actions like modifying databases or initiating payments based on hallucinations.

    Types of AI Guardrails

    Enterprises typically deploy multiple layers of guardrails:

    • Input Filters: Screen prompts for attacks.
    • Data Protection Tools: Identify and redact personal or proprietary information.
    • Content Filters: Remove hate speech and other harmful material.
    • Fact Checks: Compare outputs against trusted sources.
    • Custom Policy Rules: Enforce company-specific limits.

    Layering is critical because no single filter catches every issue. Tools vary: cloud services like AWS Bedrock Guardrails and Azure AI Content Safety handle moderation, while frameworks like NeMo Guardrails and Guardrails AI operate within applications.

    Regulatory and Audit Pressures

    Regulation is a key driver. The EU AI Act imposes fines up to 7% of global annual turnover for prohibited practices, and GDPR adds privacy obligations. Guardrail logs provide evidence for audits and align with frameworks like the NIST AI Risk Management Framework and OWASP’s top LLM risks. Deloitte’s 2026 AI report found only 20% of organizations have mature governance models, highlighting a significant gap.

    Implementation Strategies

    A layered deployment is standard. A central gateway can manage all model traffic, with cloud safety services checking inputs and specialized tools validating outputs for accuracy and attacks. Teams should treat retrieved documents and tool results as untrusted inputs. Logging every decision helps identify weaknesses and demonstrate control. Speed is crucial; some runtime tools claim to block unsafe outputs in under 200 milliseconds. Gartner predicts that by 2030, half of AI agent failures will stem from governance gaps and weak system integrations.

    Conclusion

    AI guardrails establish clear boundaries for what AI systems can see, say, and do. They reduce the risk of data leaks, false information, and rule violations while providing the audit trails regulators demand. As AI agents take on real-world tasks, guardrails transition from a nice-to-have to a necessity. Enterprises that build layered guardrails early will scale AI with greater trust and fewer surprises.

    Frequently Asked Questions

    1. What are AI guardrails?

    They are rules, filters, and checks that limit what an AI system can accept and produce. Some screen prompts, others inspect responses, catching unsafe content before it reaches users.

    2. Why do enterprises need AI guardrails?

    A single wrong answer or leaked file can harm trust, profit, and compliance. Guardrails reduce the risk of data leaks, false answers, and rule violations, and provide logs for auditors.

    3. What are the main types of AI guardrails?

    Common types include input filters, data protection tools, content filters, fact checks, and custom policy rules. Enterprises typically combine multiple layers for comprehensive protection.

    4. What is the difference between a chatbot risk and an agent risk?

    A chatbot that hallucinates gives a wrong answer. An AI agent that hallucinates can act on it, such as changing a database or triggering a payment, making guardrails more critical for agents.

    5. How can enterprises roll out AI guardrails?

    A layered plan is common: a central gateway for model traffic, cloud services for input checks, and specialist tools for output validation. Logging every decision and treating retrieved documents as untrusted inputs are also key.

  • How to Govern Agentic AI: Identity, Permissions, and Audit Trails

    How to Govern Agentic AI: Identity, Permissions, and Audit Trails

    Why Agentic AI Demands a New Approach to Governance

    Agentic AI systems don’t just generate text—they plan tasks, invoke tools, and take actions with limited human oversight. This shift from content generation to autonomous execution changes the entire risk landscape. A chatbot that merely answers questions is governed by rules for output accuracy, but an agent that books transactions, writes code, or reroutes payments requires controls over identity, permissions, and auditability. The core challenge: accountability becomes far harder to trace when an AI system acts on its own.

    Regulatory and Standards Landscape

    Formal law dedicated solely to agentic AI remains scarce. Regulators around the world are still adapting broader AI regulations to these autonomous systems, and the approach varies significantly by region.

    • European Union: The EU AI Act provides comprehensive, risk-based regulation. It imposes documentation, transparency, and human oversight duties on high-risk uses, including certain employment and credit decisions—but only when the specific application qualifies, not automatically because the system is agentic.
    • United States: No single federal AI law exists. Instead, sectoral rules apply—consumer protection statutes via the FTC, anti-discrimination laws, and state-level initiatives like Colorado’s AI accountability law.
    • Standards Bodies: Frameworks like the NIST AI Risk Management Framework (AI RMF) and ISO/IEC 42001 are filling legislative gaps. These provide structured processes for mapping, measuring, and managing AI risk, and they offer a certifiable management-system standard. Neither replaces applicable law, but both help organizations demonstrate a credible governance process.

    Five Practical Questions for Agentic Compliance

    Enterprise governance can be distilled into five actionable inquiries:

    1. Identity: Which agent performed which action, under whose authorization, using which credentials, and against which system? This becomes critical when agents interact with ERP, CRM, HR, or finance platforms—an unlogged action can create a compliance gap.
    2. Permission Scoping: Apply least-privilege access. An agent should only receive the permissions required for its assigned task. For instance, a customer-service agent might issue refunds under a certain amount but cannot change payment credentials or reset passwords.
    3. Audit Trails: Record inputs, outputs, tool calls, permissions, approvals, timestamps, and actions so you can reconstruct events later. When a loan-processing agent denies an application, regulators may ask for the decision’s basis—system logs hold up in review, not the agent’s internal reasoning.
    4. Human Checkpoints: Insert a person into high-stakes moments. A financial firm could require human sign-off before an agent executes transactions above a threshold, even if the agent can technically do it alone.
    5. Continuity: Governance isn’t a one-time certification. Regularly test for bias before launch, monitor behavior after deployment, and review permissions as the agent’s role expands.

    Responsible AI as an Ongoing Discipline

    Beyond initial testing, agentic systems need mechanisms to pause, restrict, or disable execution when unexpected behavior is detected. You cannot rely on the agent to recognize its own errors. Scenario testing—running the agent through ambiguous instructions, conflicting goals, unexpected tool responses, and attempts to exceed permissions—is often skipped but essential. Testing only routine tasks leaves harder failure modes undiscovered until they occur in production.

    Governance Must Evolve With the Agent

    The most difficult governance problem isn’t writing policy—it’s keeping it current as agents become more capable. A rulebook designed for an email-answering agent won’t suffice when the same agent starts negotiating contracts. Organizations that treat governance as a fixed checklist will fall behind. Instead, build review cycles directly into deployment, revisiting identity, permissions, and oversight every time capabilities expand. This proactive approach catches problems before they become incidents.

    Why It Matters

    Agents now move money, write code, and access sensitive systems without supervision. Without clear accountability, permission limits, and audit trails, errors scale quickly and remain invisible until damage occurs. Strong governance determines whether enterprises can trust and safely deploy these systems.

    The central question is no longer whether an AI system produces a safe answer—it’s whether your organization can control, observe, and stop what the system does. Design governance into the agent from its first deployment, with controls built to evolve alongside its permissions, tools, and responsibilities.

  • Responsible AI: Principles, Tools, and Business Impact Explained

    Responsible AI: Principles, Tools, and Business Impact Explained

    Responsible AI helps businesses manage algorithmic risks through fairness, transparency, privacy, security, human oversight, and continuous monitoring. It supports compliant, trustworthy, and sustainable AI adoption.

    What is Responsible AI?

    Responsible AI refers to the practices used to design, develop, deploy, and operate AI systems in ways that consider fairness, transparency, accountability, privacy, security, safety, and human oversight. The OECD AI Principles promote trustworthy AI that respects human rights and democratic values. Responsible AI does not guarantee a system is unbiased or error-free; instead, it establishes processes for identifying risks, testing systems, monitoring outcomes, and responding when problems emerge.

    Bias, Data, and Privacy

    Bias is a major challenge. AI models trained on incomplete or skewed data can amplify patterns, affecting recruitment, lending, healthcare, and more. Data quality is central: businesses must understand data origins, representativeness, processing, and privacy compliance. Data governance should include ownership, access controls, lineage, retention, and correction procedures. Privacy extends beyond training; organizations must consider data collection, storage, access, and potential exposure through outputs or integrations.

    Transparency and Human Oversight

    Transparency is crucial when AI influences significant decisions. Documentation should cover model purpose, limitations, data sources, evaluation results, and appropriate use. Explainability tools help users understand outputs. Human oversight allows people to review, question, or override AI outputs in high-impact applications like employment, healthcare, and credit, as required by regulations like the EU AI Act.

    Tools for Responsible AI

    Businesses can use bias-detection, fairness-testing, explainability, and model-monitoring tools. Red-teaming exposes vulnerabilities and unsafe behavior. Data-governance platforms support lineage and quality. Frameworks like NIST’s AI Risk Management Framework (Govern, Map, Measure, Manage) provide structure throughout the system lifecycle.

    Governance Does Not End at Deployment

    Responsible AI is not a one-time checklist. Models face changing data, new users, and evolving risks. Organizations should establish monitoring thresholds, incident procedures, periodic reviews, and mechanisms for retraining or withdrawing systems. NIST emphasizes continuous risk management.

    Regulation and Business Impact

    Regulations like the EU AI Act impose risk-based requirements. Industry standards and internal policies complement regulation. Strong AI governance reduces operational and legal risks, supports compliance, and maintains trust. Poorly governed systems can lead to discrimination, privacy breaches, and reputational damage.

    Building a Practical Responsible AI Strategy

    Start by assigning clear accountability, classifying use cases by risk, conducting impact assessments, and documenting models and datasets. Governance teams should establish approval processes, technical teams conduct testing, and business users receive training. The goal is to combine innovation with responsibility, enabling organizations to scale AI where benefits justify risks.

    Frequently Asked Questions

    1. What is Responsible AI?

    Responsible AI is an approach to developing and operating AI systems that considers fairness, transparency, privacy, security, safety, accountability, and human oversight throughout their lifecycle.

    2. Why is Responsible AI important for businesses?

    Responsible AI helps organizations identify potential harms, manage operational and compliance risks, protect sensitive information, and establish processes for monitoring AI systems after deployment.

    3. How can businesses detect AI bias?

    Businesses can evaluate datasets and model outputs across relevant groups, conduct fairness testing, monitor disparities, and investigate potentially discriminatory outcomes before deployment.

    4. What role does NIST AI RMF play?

    NIST’s AI Risk Management Framework provides voluntary guidance for managing AI risks through four functions: Govern, Map, Measure, and Manage.

    5. Why is human oversight important in AI?

    Human oversight allows people to review, challenge, or override AI outputs when systems influence consequential decisions or produce unexpected results requiring contextual judgment.

  • How to Build a Decision-Centered Business Intelligence Strategy That Delivers Results

    How to Build a Decision-Centered Business Intelligence Strategy That Delivers Results

    A strong Business Intelligence (BI) strategy connects trusted data, clear metrics, semantic models, AI, and governance directly to business decisions. This approach helps companies improve accuracy, speed, insight, and measurable results. Without a decision-centric focus, even the most sophisticated BI program can produce hundreds of charts yet leave leaders without clear answers.

    Start with Business Decisions

    A practical BI strategy begins with the decisions that affect revenue, costs, risk, customers, and operations. Each major decision needs a clear owner, a defined time frame, reliable data, useful metrics, an action path, and a way to measure the outcome. For example, a sales forecast gains real value when a business leader uses it to set targets, adjust a market plan, or reallocate resources. This approach transforms BI from a report factory into a decision system. Gartner’s 2026 research confirms that analytics value depends on defined, governed, and operational decisions rather than insight alone.

    Put Data Quality First

    AI cannot repair weak source data. BARC’s 2026 Data, BI and Analytics Trend Monitor, based on responses from 1,579 professionals worldwide, ranks data quality at the top of its trend list. Data security and privacy follow closely at 7.9 out of 10. A reliable BI foundation requires accurate records, clear ownership, secure access, fresh data, strong definitions, and data lineage. These controls become even more critical when AI tools access large amounts of corporate information. Poor source data can spread errors across reports, forecasts, recommendations, and automated decisions.

    Create One Business Definition

    Different teams often use the same term for different measures. Revenue, active customer, churn, margin, and forecast can each have several definitions. A semantic layer brings these definitions together through common business terms, data fields, rules, relationships, and approved metrics. Gartner’s 2026 research identifies composite semantic layers as an important direction for data and analytics, helping reduce gaps between data systems and providing stronger context for accurate AI agent results. Major BI platforms now reflect this shift: Microsoft’s June 2026 Power BI update added Fabric Apps for semantic models, and Tableau’s August 2026 release included a Semantic Model Builder with AI tools.

    Add AI with Clear Guardrails

    Generative AI helps analysts ask questions in plain language, create measures, explain trends, and find patterns. AI agents can also support data workflows and routine analysis. However, these tools need clear limits, audit trails, access rules, human review, and measurable standards for accuracy. Gartner’s June 2026 outlook lists decision governance, AI governance, and agentic data streams among major trends. The firm forecasts that explicitly modeled business decisions could achieve five times higher trust and 80% faster execution than ungoverned decisions by 2029.

    Measure Business Value

    A BI strategy needs measures that connect analytics to business results. Dashboard counts offer little proof of value. Better measures include decision cycle time, forecast accuracy, data quality, use of approved metrics, time to insight, manual report hours removed, AI answer accuracy, and financial or operational results. A mature BI program shows a clear chain from trusted data to a metric, from the metric to a decision, from the decision to an action, and from the action to a measurable result.

    Build a Decision-Centered BI Model

    The modern BI model goes beyond reports and dashboards. A stronger structure connects business goals with decisions, governed metrics, semantic models, trusted data, AI tools, and measurable outcomes. Real-time data adds value when decision speed matters, and embedded analytics places useful insights inside daily business workflows. The latest research points to one clear lesson: AI can expand the reach of analytics, but trusted data and clear business definitions remain the foundation. A strong BI strategy gains value when technology serves specific business decisions and each major insight has a clear path to action.

    Frequently Asked Questions

    1. What is Business Intelligence strategy?
    Business Intelligence strategy is a structured approach that connects business goals, trusted data, analytics, technology, and decision-making.

    2. Why does data quality matter in BI?
    Poor data can create inaccurate reports, forecasts, and AI results, while reliable data supports better analysis and stronger decisions.

    3. What is a semantic layer in BI?
    A semantic layer creates shared definitions, relationships, rules, and metrics so different teams can work with consistent business information.

    4. How does AI affect Business Intelligence?
    AI can help analyze data, answer questions, explain trends, create measures, and support analytical workflows, but strong governance and reliable data remain essential.

    5. How can companies measure BI success?
    Companies can assess decision speed, forecast accuracy, data quality, time to insight, AI accuracy, report efficiency, and measurable financial or operational results.

  • Building Trust in Agentic BI: Key Challenges and Solutions for Enterprises

    Building Trust in Agentic BI: Key Challenges and Solutions for Enterprises

    Agentic Business Intelligence (BI) moves beyond traditional dashboards by enabling AI agents to analyze data, answer natural-language questions, and even trigger automated actions. However, this greater autonomy introduces a critical question: how can businesses trust the decisions made by these intelligent agents?

    Accuracy Comes First

    Incorrect data, flawed calculations, or misunderstood business queries can quickly erode confidence. Before AI insights influence important decisions, organizations must establish reliable data foundations and rigorous validation processes.

    Data Quality Matters

    Businesses need clean, governed, and well-defined datasets so that agents can interpret metrics correctly. Clear data ownership, lineage tracking, and ongoing quality checks reduce the risk of unreliable business intelligence.

    Explainability Builds Confidence

    Decision-makers require more than just an AI-generated conclusion. They need to understand which data was used, what assumptions were made, and how the result was produced. Transparent reasoning fosters trust and enables informed judgment.

    Permissions Must Be Controlled

    Organizations should implement role-based permissions, least-privilege access, and approval controls. This ensures that agents only perform authorized tasks within clearly defined boundaries.

    Human Oversight Still Matters

    Human accountability remains essential when agents operate in critical business processes—especially when recommendations have financial, operational, or customer consequences.

    Continuous Monitoring Is Essential

    Ongoing monitoring, testing, and incident tracking help organizations detect unexpected behavior before it escalates into a larger business problem.

    Security Is a Major Barrier

    McKinsey’s 2026 AI Trust Maturity Survey identified security and risk concerns as the top barrier to scaling agentic AI. Addressing these concerns is paramount for adoption.

    Build Governance Into BI

    Governance should be designed into the system from the beginning, rather than added after autonomous agents are already deployed. Proactive governance ensures that trust is built into every layer of the solution.

  • Agentic AI Market Forecast to Reach $290.62 Billion by 2035, Driven by Enterprise Adoption and Multi-Agent Systems

    Agentic AI Market Forecast to Reach $290.62 Billion by 2035, Driven by Enterprise Adoption and Multi-Agent Systems

    The global agentic AI market is projected to surge from USD 8.19 billion in 2025 to USD 290.62 billion by 2035, registering a compound annual growth rate (CAGR) of 42.88% between 2026 and 2035, according to the Global Agentic AI Market 2026 report by Analytics Insight. The market is expected to reach USD 12.13 billion in 2026, reflecting a shift from AI systems that mainly generate content and recommendations toward systems that can plan, reason, coordinate, and execute multi-step tasks.

    The report emphasizes that the next phase of growth will depend on more capable models and their reliability, security, governance, integration, evaluation, and accountability. As enterprises increasingly deploy AI systems that can access business data, use software tools, and take action within defined limits, the market is expected to expand more than 5.8 times between 2030 and 2035.

    Agentic AI Market Growth Accelerates

    Investment conditions are helping push this forward. Stanford HAI’s 2026 AI Index lists global corporate AI spending at USD 581.7 billion, up 130% from the previous year. NVIDIA’s newest reports also point to strong growth in data center sales, with revenue up 117% year over year. At the same time, major cloud and tech firms are planning capital spending of about USD 745 billion for 2026.

    Deloitte’s 2026 State of AI in the Enterprise study, which included 3,235 executives in 24 countries, showed that 74% of companies expect to run AI agents by 2027.

    Adoption Is Still Behind Early Trials

    The report calls out a clear gap: many firms want agentic AI, but fewer are using it at full scale. McKinsey data shows 88% of companies use AI in at least one area, but only 23% have scaled agentic AI across their business. In another McKinsey survey, 62% said they were trying AI agents, yet only 23% had scaled an agentic system. No single business area reached 10% adoption at scale, suggesting most organizations are still in pilots and early testing rather than full rollout.

    Solutions Lead as Enterprises Build Agent Platforms

    The market is expected to remain solution-led during the forecast period. Agentic AI solutions are projected to increase from USD 5.12 billion in 2025 to USD 168.56 billion by 2035, while services are forecast to rise from USD 3.07 billion to USD 122.06 billion. The report attributes the strength of solutions to enterprise spending on agent platforms, orchestration software, development tools, and application-specific agents. Services are expected to gain ground as businesses require systems integration, security, governance, workflow redesign, and managed AI services for production deployment.

    Multi-Agent Systems Set to Reshape Architecture

    The report identifies a shift from standalone agents toward coordinated multi-agent environments. Single-agent systems are projected to grow from USD 5.01 billion in 2025 to USD 139.50 billion by 2035, while multi-agent systems are forecast to rise from USD 3.19 billion to USD 151.12 billion, registering a 47.09% CAGR. The transition remains in its early stages, with current enterprise deployments largely concentrated in one or two business functions. However, 85% of enterprises expect to customize agents to meet their specific requirements.

    Hybrid Deployment Records Fastest Growth

    On-premises deployment is expected to remain the largest category, increasing from USD 4.74 billion in 2025 to USD 124.96 billion by 2035. Cloud deployment is forecast to reach USD 110.43 billion, while hybrid deployment is expected to reach USD 55.22 billion. Hybrid deployment has the fastest projected CAGR at 51.05%, supported by enterprises seeking scalable AI capabilities alongside private infrastructure and controlled environments.

    IT, Cybersecurity, and BFSI Drive Expansion

    Customer support tools and virtual assistants remain the top application category, growing from about USD 2.28 billion in 2025 to about USD 61.03 billion by 2035. Other categories also grow fast: IT operations and software development are forecast to reach around USD 68.29 billion, data and analytics about USD 29.06 billion, and cybersecurity approximately USD 21.80 billion. The report also points to fast risers including cybersecurity, legal and compliance, operations and supply chain, data and analytics, and IT operations. BFSI is expected to remain the largest end-use industry in 2035.

    North America Leads, Asia Pacific Grows Faster

    North America remains the biggest market by value, at about USD 3.18 billion in 2025 and forecast to reach around USD 98.81 billion by 2035. Asia Pacific is expected to grow faster, starting at USD 2.22 billion in 2025 and reaching nearly USD 107.53 billion by 2035, with a CAGR of 47.40%. Europe is also expected to rise, from about USD 2.08 billion in 2025 to around USD 66.84 billion in 2035.

    Reliability and Governance Remain Key Hurdles

    Despite the market’s growth trajectory, reliability remains a major constraint. Stanford HAI’s 2026 AI Index indicated that agents complete around 66% of tasks successfully on OSWorld, meaning one in three attempts still fails. Gartner reported that a Fortune 500 enterprise could run more than 150,000 agents by 2028, up from fewer than 15 in 2025, while only 13% of organizations believed they had adequate governance.

    The report expects the next phase to move agentic AI beyond standalone software into enterprise workflows, digital infrastructure, and eventually physical environments. Multi-agent systems, persistent memory, robotics, vertical AI agents, and human-agent collaboration are expected to shape that transition. The broader outlook is that commercial value will increasingly depend on whether agents can perform important tasks reliably, securely, and at scale, rather than simply demonstrating what AI can do.

  • AI Agents Move Beyond Chatbots: 4 Real-World Jobs Where They Act Autonomously

    AI Agents Move Beyond Chatbots: 4 Real-World Jobs Where They Act Autonomously

    AI agents are evolving from simple question-answering tools into autonomous operators that can plan tasks, use software, verify results, and execute multi-step workflows with minimal human oversight. This shift from generating answers to completing entire processes is reshaping industries. Here are four key areas where AI agents are taking independent action in 2026.

    Financial Operations

    Financial firms now deploy AI agents for research, portfolio monitoring, risk assessments, and other complex workflows. Some systems rebalance portfolios within approved limits or handle operational exceptions automatically. Human-defined rules, permissions, and oversight remain essential for high-impact financial decisions, but routine tasks are increasingly handled by agents.

    Customer Support

    AI support agents have moved beyond scripted responses. They can classify customer requests, retrieve account data, check policies, process eligible refunds, update CRM records, send responses, and escalate unusual cases. The goal is no longer just answering a question—it’s resolving the entire customer case autonomously.

    Smart Buildings and Infrastructure

    AI agents connect with building systems, sensors, and HVAC equipment to monitor conditions and adjust operations in real time. Research from 2026 demonstrates agent-based systems that continuously optimize cooling and energy usage, showing how AI can take physical-world actions in smart buildings.

    Software and IT Operations

    Coding agents read repositories, identify relevant files, modify code, run tests, inspect failures, and prepare changes for review. IT agents investigate alerts, search logs, and handle routine fixes. While human engineers still review security-sensitive or high-impact changes, agents now manage significant portions of development and maintenance workflows.

    Setting Boundaries for Autonomous Agents

    Independent action introduces new risks: agents may act on incorrect information, receive excessive permissions, follow malicious instructions, or propagate errors across connected systems. Security experts recommend least-privilege access, detailed activity logs, continuous monitoring, rigorous testing, and human approval for high-risk actions. The transition from assistants to operators requires careful governance.

    The takeaway: AI agents are not replacing all workers overnight. Instead, they are owning narrow, repeatable workflows while humans handle exceptions, accountability, and major decisions. Finance, customer operations, software development, and smart infrastructure are leading this transformation in 2026.

  • Enterprise Agentic AI: Unlocking Benefits While Navigating Challenges and Implementation

    Enterprise Agentic AI: Unlocking Benefits While Navigating Challenges and Implementation

    Agentic AI has evolved beyond simple conversational tools. Enterprise systems can now manage multi-step workflows, tap into business databases, call software APIs, and execute actions with minimal human oversight. This shift presents a significant business opportunity, but it also forces a critical question: how much autonomy should an enterprise grant an AI system?

    The answer hinges on the task, the data involved, the associated risk, and the value at stake. Current enterprise data reveals a clear gap between interest and measurable results. McKinsey reports that nearly two-thirds of enterprises have experimented with AI agents, yet fewer than 10% have scaled them to deliver tangible value. Additionally, 80% of companies cite data limitations as a major barrier to scaling.

    From Answers to Actions

    Traditional AI tools often stop after generating text, analyzing data, or suggesting a next step. An agent can take the process further: it can review a request, check company records, use an approved system, make a decision, and complete a task. This model can support areas such as customer service, finance, sales, legal work, procurement, and IT. The value comes from the full workflow rather than a single response.

    OpenAI enterprise data shows how fast this shift has grown. In June 2026, agentic use made up 64% of combined enterprise output tokens from Codex and ChatGPT. Weekly active Codex users also grew across functions outside software development, including legal, sales, recruiting, and marketing.

    Specialized Agents Deliver Stronger Returns

    Enterprise leaders now have clearer evidence about where agents can create value. Gartner found that specialized, domain-focused agents offer the strongest path to measurable returns. Gartner predicts that specialized agents will produce 80% of tangible agentic AI return on investment by 2028.

    A parts-order process offers a useful example. One industrial services deployment produced about USD 3 million in annual return and freed 90,000 technician hours. The result came from a narrow business task rather than a broad AI project. This approach gives enterprises a practical lesson: a focused agent with clear authority can create more value than a general system with access to many unrelated tasks.

    Data and Security Remain Major Barriers

    An agent needs reliable information to make sound decisions. Many large companies still keep data across separate databases, older software, and isolated departments. Poor data quality, weak access rules, and unclear data ownership can limit agent performance. Security also takes on a new role. A normal application may wait for a person to approve an action. An autonomous agent can decide and act within seconds, creating a need for clear rules around identity, permissions, audit records, and financial limits.

    The World Economic Forum has highlighted agent authorization, delegation policy, monitoring, and accountability as key areas for trusted enterprise use. Its work also proposes an Agent Capability and Authorization Profile to help enterprises define what an agent can access and what actions it can take.

    Agent Sprawl Creates New Management Problems

    More agents do not always mean more value. Gartner predicts that the average Fortune 500 enterprise could have more than 150,000 AI agents by 2028, compared with fewer than 15 in 2025. Only 13% of organizations currently believe they have suitable agent governance. Such growth can create duplicate tools, unclear ownership, excessive permissions, and higher technology costs. Enterprises therefore need a central control layer that can track agents, manage access, and record key actions.

    Cost control also needs attention. KPMG found that 26% of organizations have real-time visibility into AI operating costs. Without that view, a company may know how many tasks an agent completes but not the true cost of each successful result.

    A Safer Path to Enterprise Adoption

    A strong enterprise plan should start with one valuable workflow. The company can first measure task cost, processing time, error rates, and business results. A controlled pilot can then test the agent with limited data, tools, and permissions. Human review should remain part of high-risk tasks such as major financial decisions, contract approval, or production system changes. Low-risk work, such as document summaries or internal ticket creation, can support greater autonomy.

    Deloitte found that 74% of leaders expect almost half of their business processes to undergo redesign around AI agents within four years. Yet only 5% say their current processes show high readiness for AI agents, while just 15% have scaled orchestrated, cross-functional multi-agent use. That gap defines the real enterprise challenge. Agentic AI does not need more hype; it needs better process design, stronger data, clear authority, and measurable business value. The companies that connect those pieces can turn AI agents from experimental software into a controlled digital workforce.

    Frequently Asked Questions

    What is Agentic AI for enterprises?

    Agentic AI refers to AI systems that can handle multi-step tasks, use business tools, and take actions with limited human input.

    What benefits can Agentic AI offer businesses?

    Agentic AI can improve productivity, reduce process costs, speed up decisions, and support tasks across areas such as sales, finance, legal work, customer service, and IT.

    What are the main challenges with enterprise AI agents?

    Key challenges include poor data quality, security risks, unclear permissions, reliability concerns, high costs, and weak governance.

    Should enterprises give AI agents full autonomy?

    Full autonomy may suit low-risk tasks, while high-risk activities should retain human review and strict approval controls.

    How should a company start with Agentic AI?

    A company should select one valuable workflow, set clear goals, establish a baseline, limit agent permissions, and measure results before wider deployment.

  • Agentic AI in Indian Banking: From Chatbots to Autonomous Decision-Making

    Agentic AI in Indian Banking: From Chatbots to Autonomous Decision-Making

    Artificial intelligence in Indian banking has largely meant chatbots that answer balance queries, recommendation engines that suggest the next product, and fraud models that flag suspicious transactions for a human to review. That era is ending quickly. What is emerging now is agentic AI: a class of systems that does not just respond to a prompt, but plans, decides and acts across multiple steps without waiting for a human to approve each move.

    The shift is not cosmetic. It changes how credit gets underwritten, how KYC gets verified, how fraud gets stopped, and how service teams spend their day. The numbers behind it are large enough to demand attention. The operational details are messy enough to demand caution.

    From Prompt-Response to Plan-and-Act

    Traditional automation in banking, including robotic process automation and early generative AI tools, worked on a simple pattern: a human triggers a task, the system executes a fixed script, and the output goes back to a human for the next step. Agentic AI breaks that pattern. An agent is given a goal—something like “resolve this customer dispute” or “underwrite this loan application”—and then independently queries APIs, pulls data from multiple systems, applies reasoning and takes the next action, often chaining several steps together before a human ever sees the result.

    This matters technically because RPA breaks the moment an interface or a data format changes. Agentic systems, built on reasoning loops that plan, act and adjust based on outcomes, can handle edge cases a rules-based script cannot. That flexibility is precisely why banks are willing to give these systems more autonomy, and precisely why the risk profile looks different from anything that came before.

    The global market for agentic AI in financial services is estimated at close to $7.8 billion in 2026, up from around $5.5 billion a year ago, on a path toward more than $43 billion by 2031. That implies a compound annual growth rate above 41 percent. Even accounting for the usual noise in market-sizing reports, growth at that scale signals genuine capital commitment rather than marketing enthusiasm.

    More telling than the headline number is the adoption curve inside institutions. Around 44 percent of financial services teams report actively using agentic AI in 2026, several hundred percentage points higher than early 2025. Among the largest global banks, more than seven in ten now have programs that have moved past proof-of-concept into production or advanced piloting. Fintechs and neobanks, unburdened by decades-old core banking systems, are moving faster still. A parallel market has emerged around governance: platforms that monitor, audit and constrain what autonomous agents are allowed to do are already valued near $9 billion in 2026 and expected to cross $14 billion within five years. That the oversight layer is growing almost as fast as the core technology tells you banks understand autonomy without control is not a viable strategy in a regulated industry.

    Where Agentic AI Is Actually Being Used

    Fraud detection and anti-money laundering account for the largest functional share of agentic deployments, roughly a third of all use cases by some estimates. Fraud patterns shift constantly, transaction volumes are enormous, and the cost of a missed signal is high. Agents that correlate cross-border transaction patterns, flag anomalies and take a first action such as placing a temporary hold offer a meaningful edge over static rule engines.

    Credit underwriting has moved from experimental to operational. Rather than a loan officer manually pulling GST filings, bank statements and alternate data sources, an agent queries multiple verification APIs in parallel and produces a draft underwriting memo within seconds. The human role shifts from gathering data to reviewing a structured recommendation.

    Onboarding and KYC verification follow a similar pattern. Multi-agent architectures orchestrate biometric de-duplication, registry lookups against systems like CKYC, and fraud checks simultaneously instead of sequentially, cutting what used to take hours down to near real time. For insurers, agentic workflows validate first-notice-of-loss claims, cross-check damage documentation and trigger payouts on small claims without human intervention.

    This is no longer confined to individual institutions. NPCI is developing a Unified Agent Protocol that would let verified AI agents execute UPI payments without the user approving every transaction, having already piloted agentic payments publicly at the last Global Fintech Fest. When the country’s payment rails are themselves being redesigned for agents, the question for banks is not whether to participate but how quickly they can be ready.

    Across these use cases, institutions report autonomous resolution rates exceeding 80 percent for structured tasks such as dispute triage and routine compliance checks. That is a real productivity gain, but it carries a specific risk. When 80 percent of the easy work disappears, what remains is disproportionately the hard, ambiguous and emotionally charged work that agents are not yet trusted to handle alone. Support staff are left with an inbox of complex disputes and fraud complaints from customers who have already been through an automated flow that failed them. Industry estimates put the AI and data skills gap inside BFSI global capability centres at around 42 percent, meaning a significant share of the workforce lacks the combination of financial domain knowledge and technical fluency these systems demand.

    The Design Problem Hiding Inside the Technology Problem

    Most of this conversation treats agentic AI as an engineering problem. It is at least as much a design problem. Autonomy only creates value if a customer can understand what an agent is about to do on their behalf, and a supervisor can see why it did what it did. That is interface work: consent screens that make agent permissions legible rather than buried inside a mandate flow, explanations that surface the two or three factors behind a credit decision instead of a confidence score, and override controls that are obvious under pressure rather than three taps deep.

    In Indian retail banking, where a large share of users transact in a second language on an entry-level device, this is not polish. It is the difference between an agent people trust with a payment and one they switch off. Banks that ship autonomy without designing the visible layer around it will find adoption stalling for reasons no amount of model retraining can fix.

    Security and Governance Cannot Be an Afterthought

    Giving an autonomous agent the ability to query core banking systems, move funds or freeze accounts introduces a new category of cybersecurity concern. Agent permissioning, meaning precisely defining what each agent may do and rate-limiting how often it can act, is now a primary vulnerability that did not exist in the same form when humans initiated every transaction. Meanwhile fraud itself is becoming more sophisticated, with a large share of advanced attempts involving generative AI or synthetic voice, pushing banks to deploy defensive agents that evaluate behavioural biometrics and liveness signals in real time.

    Regulators in India have been explicit that autonomy does not remove accountability. Under SEBI’s updated Cybersecurity and Cyber Resilience Framework, regulated entities such as brokers, asset managers and depositories remain directly liable for the actions of their AI systems, closing off any defence built around blaming the algorithm. The Reserve Bank of India has taken a similarly clear position that high-stakes decisions, including credit rejections, loan restructuring and account closures, must retain a human in the loop and remain explainable, even as agentic systems handle the surrounding workflow. India’s data protection framework adds another layer, requiring that every autonomous action, data query and API call an agent makes be logged into an auditable trail a human can review after the fact.

    Agentic AI in BFSI is not a distant trend. It is already running fraud checks, assembling credit memos and triaging disputes inside real institutions today, and it is moving into the payment rails themselves. The technology has proven it can compress work that used to take hours into seconds. What remains unresolved is whether BFSI organizations can build the governance, workforce readiness and design discipline to match the pace of deployment.

    The institutions that get this right will be the ones treating agentic AI as a governance, people and design problem as much as a technology problem, measuring success not by how much work an agent completes on its own, but by how well the humans on both sides of it—customers and supervisors alike—can understand, correct and take responsibility for what it does.