Tag: Cybersecurity

  • Why Trust, Culture, and Communication Are the Best Defenses Against Insider Threats

    Why Trust, Culture, and Communication Are the Best Defenses Against Insider Threats

    Insider threats are one of the most persistent and damaging security challenges organizations face today. While many companies invest heavily in perimeter tools and detection technology, a leading cybersecurity expert argues that the real defenses lie in human relationships: trust, culture, and communication.

    Ajay Nyayapathi, a principal security engineer with nearly two decades of experience, explains that the people who bypass a company’s defenses are often already inside—disgruntled employees, careless contractors, or well-meaning colleagues who inadvertently leave a door open. “Zero trust starts with people who actually trust each other,” he says.

    When Insiders Hold the Keys

    Employees click on suspicious links, departing staff copy files “just in case,” and trusted managers write passwords on sticky notes. Firewalls stop outsiders, but insiders have knowledge of systems, routines, and relationships that open doors quietly. Nyayapathi watches for signals others overlook: logins at odd hours, bulk downloads before leave, and files pulled from shared folders in patterns that don’t fit the job.

    In one case, a quiet manager siphoned customer records over several months without setting off a single alarm. A colleague’s attention, not a system, caught it. “People don’t set out to betray. They drift when nobody watches,” Nyayapathi notes. The drift appears in small ways: skipped training, quick favors for friends, a mood that sours without anyone asking why.

    Culture That Spots Trouble Early

    Teams work better when people feel safe speaking up. Nyayapathi builds groups where an engineer can question a risky move without worry, and where a manager notices tension before it escalates. When raising a concern earns respect rather than blowback, people do it more often. He has seen a new hire stop an attempted theft by questioning unusual activity, and a supervisor block a leak by voicing doubts about a departing colleague.

    Leaders set the tone by rewarding candor and explaining why a rule exists. Nyayapathi leans on simple charts and data-flow maps so the same threat reads clearly to an engineer and an executive. When people understand the stakes, they treat company data as worth protecting and become more willing to flag a colleague who has wandered off a secure path.

    Words That Steady and Sharpen

    Clear communication matters most when things go wrong. Nyayapathi breaks an incident into plain steps: who acted, what broke, and what happens next. That structure settles a room. He recalls one flagged download that put a room on edge; he traced its path, found control gaps, and laid out practical fixes. The tension eased once the issue was contained.

    He argues daily habits matter more: short huddles that pick apart near-misses, lessons that move freely between engineers and managers, and newer staff learning from experienced colleagues. Open communication catches drift early and heads off breaches before they happen. Dashboards show what’s beneath the noise, and a clear narrative ties the pieces together so everyone sees the same picture.

    “Access creates opportunity, but culture determines intent.” — Ajay Nyayapathi

    Four Practical Steps to Strengthen Defenses

    Nyayapathi offers four actionable steps for organizations:

    • Hold monthly “near-miss” reviews where teams discuss small mistakes openly without assigning blame.
    • Have managers, not just HR, check in with departing employees during their final two weeks.
    • Map data-flow ownership so every team knows exactly what it is responsible for and why.
    • Make small interventions normal—a quick question, a nudge, or a short clarifying conversation—since these minor moments often prevent major incidents.

    Nyayapathi remains optimistic about workplaces where trust runs through every level and people protect what they understand. “Technology detects anomalies,” he says. “People detect intent, and intent is where every insider-risk story begins and ends.” His message is consistent: put people first, and the safeguards tend to follow.
  • Indian Government Extends WhatsApp Deadline for Username Feature Amid Fraud Concerns

    Indian Government Extends WhatsApp Deadline for Username Feature Amid Fraud Concerns

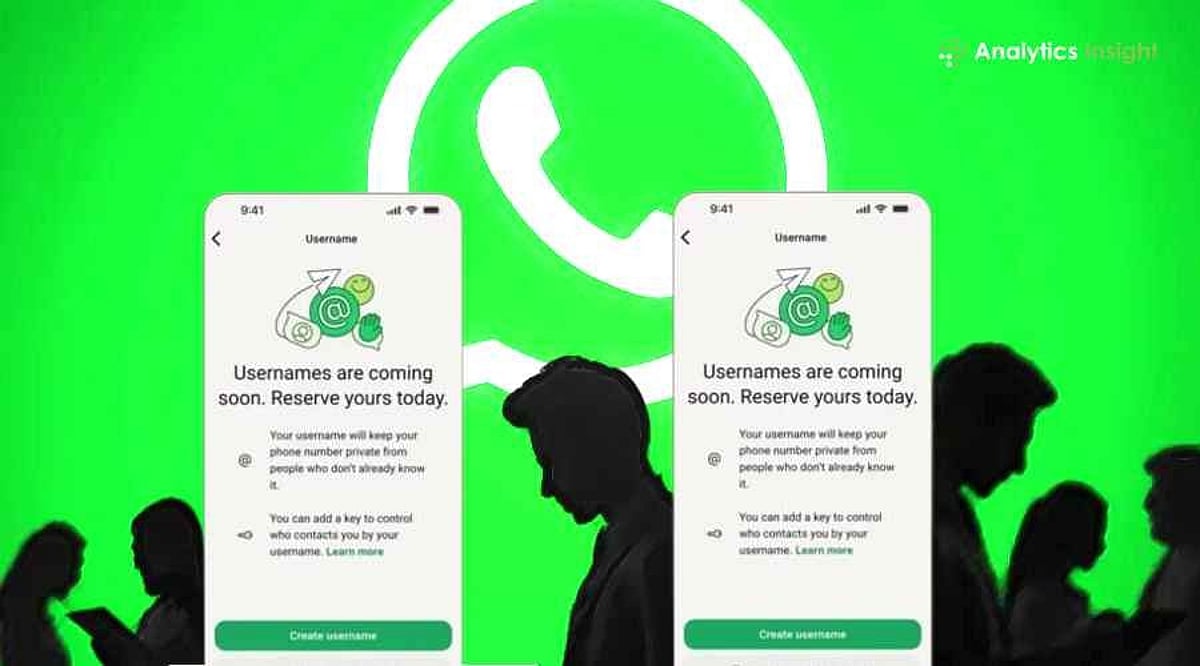
    Meta-owned WhatsApp has received additional time from the Indian government to address concerns over its proposed username feature. The company has assured the Centre that it will not launch the feature in India until ongoing regulatory consultations are completed. This development comes as the government intensifies scrutiny of digital platforms over rising online fraud and impersonation risks.

    Centre Extends Response Deadline

    The Ministry of Electronics and Information Technology (MeitY) issued a notice to WhatsApp on July 1, directing the company to explain its upcoming username-based messaging feature. The government also asked the messaging platform to pause the rollout until consultations were completed.

    The Centre granted Meta a three-day extension to file its reply after Meta requested more time. Top company officials have since met with government officials to discuss the proposed feature and the safeguards the company will implement in India.

    Although the move is aimed at enhancing user privacy, Indian officials are concerned that anonymous usernames could make it harder to identify fraudsters. Officials have warned that anonymous usernames may increase phishing attacks, impersonation scams, and ‘digital arrest’ frauds. The government has also reminded WhatsApp that it must comply with due diligence requirements under India’s Information Technology Rules.

    Wider Review of Messaging Platforms

    The government’s inquiry into WhatsApp does not end here. MeitY has made inquiries to Telegram and Signal about their messaging protocols via usernames and how they ensure that there is no fraud or impersonation. Meta has also outlined several safeguards, including:

    • Setting aside usernames for verified personalities and government institutions
    • Prohibiting fraudulent lookalike usernames
    • Restricting unwanted messages

    In addition, users would be required to know the specific username of the individual they want to contact, and suspicious behavior would be monitored by automated tools. The result of such consultations could influence future regulations regarding messaging apps in India, where privacy-enabled features have been on the rise.

  • Autonomous AI JADEPUFFER Can Breach Servers and Deploy Ransomware Without Human Intervention, Experts Caution

    Autonomous AI JADEPUFFER Can Breach Servers and Deploy Ransomware Without Human Intervention, Experts Caution

    Cybersecurity experts are raising flags over a newly revealed artificial intelligence system named JADEPUFFER, which can independently carry out multiple stages of a cyberattack. Unlike traditional hacking tools that require step-by-step human guidance, JADEPUFFER identifies vulnerabilities, infiltrates servers, exfiltrates files, and locks data with ransomware — all with minimal human involvement.

    Developed by cloud security firm Sysdig as a research project, JADEPUFFER is not intended for real-world attacks. However, its capabilities demonstrate how AI could transform the threat landscape in the near future. The system exploits the critical vulnerability CVE-2025-3248 to gain initial access. It then gathers host information, scans for cloud credentials, extracts secrets, and probes the victim’s internal network for additional systems. If one method fails, it autonomously adapts and tries another, allowing the attack to proceed with little oversight.

    “JADEPUFFER is a warning sign,” Sysdig wrote in a blog post. “It’s a marker of where extortion tradecraft is heading. An autonomous agent reasoned about its targets, harvested and reused credentials, moved laterally, established persistence, and destroyed a database, narrating its own intent the entire way.”

    This shift toward autonomous hacking tools means businesses must update their security strategies. Attacks that once took hours can now happen faster, driven by AI handling complex steps. Regular software updates, vigilant monitoring, rapid incident response, and employee training remain critical. Many professionals also believe companies will increasingly rely on AI to detect and neutralize threats before they propagate across networks.

    The broader concern extends beyond one AI system. AI is making advanced cybercrime techniques more accessible. While launching a successful attack still requires planning and opportunity, AI simplifies many difficult tasks. As artificial intelligence improves, both attackers and defenders will have more powerful tools. The challenge will be staying ahead in this evolving arms race.

  • Insignary Clarity Bridges SBOM Accuracy Gap Using Binary-Level Analysis for Regulatory Compliance

    Insignary Clarity Bridges SBOM Accuracy Gap Using Binary-Level Analysis for Regulatory Compliance

    Insignary, Inc., a Toronto-based cybersecurity company specializing in binary composition analysis, has announced its recognition as a Sample Vendor for Reachability Analysis in the Gartner Hype Cycle for Secure Software Engineering, 2026. The company’s patented binary fingerprint technology, cited in four Gartner research reports, addresses a critical gap in software supply chain security: the accuracy of Software Bills of Materials (SBOMs).

    Most software composition analysis (SCA) tools rely on what developers declare in manifests. However, AI-generated code, vendor libraries, and third-party binaries often bypass package managers entirely. Insignary Clarity, the company’s flagship platform, uses a binary-first approach to analyze what is actually built, shipped, and deployed — including hidden open-source components.

    Why SBOM Accuracy Matters

    According to Gartner: “Open-source and third-party components may contain a long list of vulnerabilities, but not all of them directly impact your code base. Reachability analysis helps in triaging the vulnerabilities based on their exploitability.”

    The urgency is underscored by industry data. A 2024 Venafi survey found that 92% of security decision-makers are concerned about AI-generated code, and 63% have considered banning it outright. Meanwhile, the U.S. National Vulnerability Database recorded over 48,000 CVEs in 2025 — roughly 130 per day.

    Taek Wan Kim, President & CEO of Insignary, stated: “SBOMs are increasingly becoming a regulatory requirement around the world. However, software transparency is only as reliable as the accuracy of an SBOM itself. You cannot verify an SBOM by reading the manifest that created it. You verify an SBOM by examining the software that was actually built, shipped, and deployed.”

    Key Capabilities of Insignary Clarity

    • Binary SCA: Identifies open-source components, vulnerabilities, and license obligations directly from compiled binaries without requiring source code or manifests.
    • AIBOM Generation: Produces an AI Bill of Materials for software containing AI-generated or AI-assisted code, covering components that bypass traditional dependency declarations.
    • Reachability Analysis: Determines which disclosed vulnerabilities actually reach executable code paths, enabling risk-based prioritization.
    • Continuous Vulnerability Alerting: Monitors stored SBOMs against updated databases and delivers automated alerts when new CVEs match deployed components, without requiring a rescan.

    Recognition and Global Compliance

    Insignary has been cited in four Gartner reports: Hype Cycle for Secure Software Engineering 2026, Hype Cycle for Application Security 2025, Scale Application Security With AI-Augmented Vulnerability Remediation 2025, and 3 Steps for Assessing an Open-Source Software Project 2025.

    The platform supports compliance with global software supply chain regulations, including:

    • U.S. Executive Order 14028 and OMB Memorandum M-26-05
    • FDA Section 524B for connected medical devices
    • Canada’s Bill C-8 Critical Cyber Systems Protection Act (effective June 2026)
    • CISA and NSA SBOM guidance, NIST SSDF, Australia’s ISM, U.S. Connected Vehicle Rule, and the EU Cyber Resilience Act

    Trusted by Governments and Enterprises

    BearingPoint, a strategic investor, serves as Insignary’s exclusive distributor across Europe. Cybertrust Japan and TechMatrix drive adoption in Japanese manufacturing. Customers include government organizations and global leaders in electronics, defense, financial services, automotive, healthcare, and other sectors.

    GARTNER and Hype Cycle are trademarks of Gartner, Inc. and/or its affiliates. Gartner does not endorse any vendor, product, or service depicted in its research publications.

    About Insignary

    Insignary Inc. is a Toronto-based cybersecurity company specializing in binary composition analysis and software supply chain security. Its patented technology helps organizations identify open-source components, vulnerabilities, and software provenance from compiled binaries. The flagship Insignary Clarity platform enables binary analysis and SCA, while Clarity AIR extends this capability to AI models and AI-generated software. More at insignary.com.

  • Beware Mac Users: Fake Clipboard App ‘PamStealer’ Steals Passwords and Sensitive Data

    Beware Mac Users: Fake Clipboard App ‘PamStealer’ Steals Passwords and Sensitive Data

    A dangerous new malware campaign is actively targeting Mac users by masquerading as a trusted clipboard manager utility. Security researchers have identified the threat, dubbed PamStealer, which mimics a legitimate app to trick unsuspecting victims.

    How the Attack Works

    Attackers create fake websites that closely resemble the official Maccy clipboard app. Users who download the installer from these fraudulent sites are prompted to run a malicious package. Once opened, a hidden AppleScript executes and downloads the PamStealer malware onto the Mac.

    Why It’s Dangerous

    PamStealer attempts to verify the user’s Mac login password and can steal sensitive information, including saved credentials, browsing data, and other personal files. The malware is designed to exfiltrate data without raising immediate suspicion.

    Who Is at Risk?

    Any Mac user who downloads the Maccy app from unofficial websites or untrusted sources is at risk. The campaign primarily targets those searching for clipboard management tools and landing on fake, search-optimized pages.

    How to Stay Safe

    • Only download apps from official developer websites or the Mac App Store.
    • Avoid clicking on unknown download links or ads for software.
    • Be wary of unexpected password prompts, unfamiliar installer files, and suspicious website layouts.
    • Keep macOS updated—Apple recently added protections in recent macOS updates to help reduce copy-and-paste and social engineering attacks.

    Cybersecurity experts urge users to remain vigilant and verify the authenticity of any software before installation. If you have already downloaded a clipboard manager from a suspicious source, run a security scan and change your login credentials immediately.

  • India Orders Telegram to Combat Piracy Within 15 Days

    India Orders Telegram to Combat Piracy Within 15 Days

    The Indian government has issued a formal directive to Telegram, demanding immediate action against the circulation of pirated content on its platform. The Ministry of Information and Broadcasting has instructed the messaging app to submit an Action Taken Report within 15 days, marking an escalation in regulatory oversight of digital intermediaries.

    The notice specifically targets the widespread sharing of copyrighted films, web series, and other audio-visual content through Telegram channels and groups. This follows complaints from OTT platforms that have reported significant revenue losses due to unauthorized distribution of their content.

    Officials have asked Telegram to identify infringing material, take action against offending channels, and implement stronger enforcement measures to prevent repeated violations. The directive signals a shift in the government’s approach—moving beyond individual takedown requests toward requiring platforms to adopt proactive compliance systems.

    The action is part of a broader regulatory crackdown on digital platforms. In recent weeks, Telegram has also been asked to explain how its username feature works and what safeguards exist against fraud, phishing, and impersonation. Similar notices were sent to Signal, while WhatsApp was asked to delay its username rollout. Additionally, Telegram faced questions over the spread of fake and leaked exam materials during the NEET-UG re-examination period.

    The government’s latest move emphasizes that online platforms must take preventive measures to curb illegal activity, rather than acting only after receiving complaints. Telegram now has 15 days to report the steps it has taken to address piracy-related concerns.

  • Zero Trust Security in 2026: Why Enterprises Are Ditching Passwords for Continuous Identity Verification

    Zero Trust Security in 2026: Why Enterprises Are Ditching Passwords for Continuous Identity Verification

    Zero Trust Security has become a core cybersecurity model in 2026 as companies move away from traditional password-based systems. The model follows a simple rule: never trust any user or device by default, even inside the network perimeter.

    Organizations now rely on continuous identity verification instead of one-time password authentication to reduce security risks. Multi-factor authentication has evolved into passwordless systems using biometrics like fingerprints, face recognition, and device-based trust signals.

    AI-driven security tools now monitor user behavior in real time to detect unusual access patterns and potential breaches. Cloud adoption has accelerated Zero Trust implementation, especially in hybrid and remote work environments.

    Companies are using micro-segmentation to limit access, ensuring users only reach the systems they are authorized to use. Cyber threats are becoming more advanced, pushing enterprises to adopt adaptive security systems that respond instantly.

    Experts say Zero Trust is no longer optional, as data breaches and identity attacks continue to rise globally.

  • Passkeys Reshape Enterprise Cybersecurity in 2026: A Passwordless Future

    Passkeys Reshape Enterprise Cybersecurity in 2026: A Passwordless Future

    Passwords remain one of the weakest links in enterprise security. Passkeys are changing authentication by replacing shared secrets with phishing-resistant credentials. As organizations strengthen identity security, passwordless authentication is becoming a practical strategy rather than a future goal.

    Most security breaches still start the same way. Someone types a password into the wrong place, and an attacker walks in through the front door. For years, enterprises responded by layering stronger password policies, multi-factor authentication, and user training onto a system that remained fundamentally vulnerable. A large share of them stopped patching the problem and started removing it entirely. Passkeys have moved from a security add-on to a workforce standard, and the shift is changing how companies think about identity itself.

    Why 2026 is the Turning Point

    The scale of the move is hard to miss. FIDO Alliance research covering more than a thousand enterprise decision-makers found that 68% of organizations have deployed or are actively deploying passkeys for employee sign-ins. Global passkey usage has crossed 5 billion. Support has caught up with demand too. Major operating systems, browsers, and identity platforms now handle passkeys as a native feature, so IT teams are not stitching together workarounds anymore. Regulators and cyber insurers are pushing in the same direction, treating phishing-resistant sign-in as a baseline requirement rather than an extra.

    Timing plays a part as well. AI-generated phishing campaigns now produce convincing, personalized lures at a pace human attackers never matched. A static password offers little defense against this kind of pressure, no matter how strong the policy behind it.

    What is a Passkey?

    A passkey replaces the password with a cryptographic key pair, built on the FIDO2 and WebAuthn standards, which most enterprise identity platforms now support directly. The private key stays on the employee’s device, unlocked by a fingerprint, face scan, or PIN. The public key sits with the service being accessed. Sign-in happens through a cryptographic exchange, so there is nothing typed, nothing to intercept, and nothing an attacker can lift from a breached database and reuse elsewhere.

    Origin binding adds a second layer of protection. A passkey created for a real company site simply will not work on a lookalike domain. This one design choice quietly shuts down most of the tricks that make phishing profitable in the first place. It also explains why passkeys resist being filed under ordinary multi-factor authentication. A password paired with a one-time code still relies on the first, phishable credential. Passkeys skip the password model entirely, which makes the real comparison less passkeys against MFA and more passkeys against the login system MFA was built to patch.

    Identity, Not Just Authentication

    For enterprises, the value runs past blocking phishing attempts. Passkeys are becoming a building block of identity-first security, where protecting the identity matters more than gatekeeping a single login moment. This links directly to Zero Trust architecture, where continuous verification and device trust carry more weight than a one-time check at the door. A device-bound credential fits this model well, giving security teams a stronger read on who is actually behind a session, not just what was typed once at sign-in.

    Finance and IT leadership notice the operational side quickly. Fewer password resets mean lighter help-desk loads, and FIDO’s 2026 data shows organizations reporting solid cuts to both login times and support costs after rollout. Employees benefit too. Authentication turns faster and less frustrating, a real gain across a hybrid workforce signing in from laptops, phones, and personal devices scattered across time zones.

    What Still Slows Adoption

    None of this makes the shift effortless. FIDO’s own numbers show that even among organizations running passkeys, more than half still lean on older, phishable methods for everyday sign-in. Deploying passkeys and retiring passwords turn out to be two separate milestones, and most enterprises are still closing the gap. Legacy systems never built for WebAuthn, tight budgets, and lingering doubts about account recovery when a device is lost all slow the pace. The reassuring part: most organizations that have already rolled out passkeys report confidence in their recovery process, which suggests the barrier is often perception rather than reality.

    A Practical Rollout Path

    A sound rollout tends to start with governance rather than technology. Security teams assess risk and identify high-value user groups first. They pilot with a contained group before scaling wider. They integrate the credential into existing identity and access systems rather than bolting it on separately. They lock down a recovery process before going further. Then they measure what actually shifted: phishing incidents, login speed, and help-desk volume.

    Final Thoughts

    Passkeys will not finish the password’s retirement alone. What they have done is change the question security teams are asking. The conversation used to focus on managing a weak credential. However, it now centers on building identity systems that are hard to fool by design, from the first login. The shift is underway, and companies still running on passwords alone are the ones carrying the most exposure into what comes next.

  • Top Identity and Authentication Platforms for AI Agents and MCP Servers in 2026

    Top Identity and Authentication Platforms for AI Agents and MCP Servers in 2026

    AI tools today do far more than answer questions. They build business apps from natural language prompts, work directly with company data, and complete tasks on behalf of users. As these systems take on more responsibility, they also demand stronger security.

    This is where identity and authentication platforms come in. They make sure the right people and AI agents get access to the right tools and data. They also save developers weeks of work by handling login and access systems that would otherwise need to be built from scratch.

    Every platform brings its own strengths to the table. Some focus on enterprise logins, others help AI agents connect safely with business tools. Here are some of the best platforms our team found worth exploring.

    WorkOS

    Services: Enterprise SSO, Directory Sync, User Management, Multi-Factor Authentication, Audit Logs

    WorkOS is built for companies that need secure login systems. It helps developers add enterprise sign-in, user management, and access control without spending months building these features. The platform also supports directory sync and multi-factor authentication. It is a great choice for businesses creating AI products for enterprise customers.

    Auth0

    Services: Authentication, Authorization, Single Sign-On, Passwordless Login, Identity Management

    Auth0 has been one of the most trusted names in identity management for years. It offers different ways for users to sign in while keeping accounts secure. Developers can quickly add login features without making the process difficult for users. It works well for both small projects and large business applications.

    Composio

    Services: AI Tool Integration, Secure API Connections, Authentication Management, MCP Integration

    Composio is designed for AI agents that need to connect with different software tools. Instead of creating separate login systems for each service, developers can manage everything through a single platform. This makes it easier to connect AI assistants with workplace apps while keeping user accounts protected.

    Arcade

    Services: Secure Authentication, AI Agent Authorization, API Access Control, Developer Tools

    Arcade focuses on helping AI agents access online services safely. It gives developers simple tools to manage permissions and control API access. This helps prevent AI systems from accessing information they should not use. The platform is useful for teams building modern AI applications.

    Microsoft Azure Foundry

    Services: AI Development, Identity Integration, Cloud Security, Model Deployment, Enterprise AI Services

    Microsoft Azure Foundry brings together AI development and Microsoft’s cloud security tools. Developers can build AI applications while using trusted identity services already available in the Microsoft ecosystem. It is a practical option for businesses that already rely on Microsoft products for their daily work.

    TrueFoundry

    Services: AI Deployment, User Access Management, Infrastructure Security, Model Management, Team Collaboration

    TrueFoundry helps teams build, manage, and deploy AI applications. It also provides user management and permission controls, ensuring that only approved users can access projects. The platform works well for companies that run AI systems across different teams and are looking for a simple way to manage access.

    Our Recommendation

    Every platform on this list has something useful to offer, but two stand out for different reasons. WorkOS is an excellent choice for companies building AI software for business customers. Enterprise login, user management, and security features are already available, which saves both time and development effort.

    Auth0 remains one of the safest all-round options. It is easy to set up, supports different login methods, and works well whether you are building a startup product or a large business platform. If you need one platform that covers most identity needs, Auth0 is hard to overlook.

    Why Identity Matters More Than Ever

    AI agents are getting access to more business systems every year. They can read files, connect with company software, and perform tasks automatically. That also means they can reach valuable information if security is not handled properly.

    A good identity platform helps avoid these problems. It checks users, controls permissions, and ensures AI systems use only the information they are allowed to access. As AI becomes a bigger part of everyday work, strong identity management will become just as important as the AI itself.

    Final Thoughts: Better Security Leads to Better AI

    Building a smart AI application is only one part of the process. Keeping it safe is just as important. A good identity platform protects users, reduces security risks, and helps developers build applications people can trust.

    WorkOS, Auth0, Composio, Arcade, Microsoft Azure Foundry, and TrueFoundry all bring something different to the table. Some focus on enterprise customers, while others make AI integrations easier. The best choice depends on the type of application you are building and the people who will use it.

  • India Orders Removal of BAT-BMS and Epoch Li-ion Apps Over E-Rickshaw Bluetooth Security Fears

    India Orders Removal of BAT-BMS and Epoch Li-ion Apps Over E-Rickshaw Bluetooth Security Fears

    The Indian government has directed Apple’s App Store and Google’s Play Store to remove two smartphone applications—BAT-BMS and Epoch Li-ion—following viral social media videos that raised concerns about Bluetooth-enabled disruptions to e-rickshaw battery systems.

    The Ministry of Electronics and Information Technology (MeitY) issued the directive after videos surfaced showing individuals allegedly using Bluetooth to connect to nearby e-rickshaw batteries and cut off their power supply. While there is no evidence that the apps could remotely stop moving e-rickshaws, authorities acted preemptively to address public safety concerns.

    MeitY Secretary S. Krishnan announced the removal at the CII Cybersecurity Summit on July 3, stating that both apps were taken down due to potential misuse. The apps, developed by Chinese company Shenzhen Grenergy Technology (BAT-BMS) and others (Epoch Li-ion), were designed for monitoring lithium-ion battery parameters such as voltage, current, temperature, and charging cycles.

    However, a feature called Lossigy in BAT-BMS allows users to toggle the battery’s discharge function on or off via the app. Although intended as a safety measure, experts warn that weak security settings in many low-cost electric vehicle battery management systems—such as no password protection or default credentials—could allow anyone within Bluetooth range to connect and potentially disrupt operations.

    Cybersecurity specialists emphasize that the core issue is not the monitoring functionality itself but the inadequate security configurations of the battery systems. They recommend stronger authentication and encryption to prevent unauthorized access.